Unknown's avatar

About charlesarthur

Freelance journalist - technology, science, and so on. Author of "Digital Wars: Apple, Google, Microsoft and the battle for the internet".

Start Up No.927: doubts over Bloomberg, Google call screening, iPad Pros with Face ID?, the ongoing piracy problem, and more


Apple’s retail store in Shenzhen: site of a sizable triad-driven fraud in the years up to 2013. Photo by Chris on Flickr.

A selection of 10 links for you. Since you’re here. I’m @charlesarthur on Twitter. Observations and links welcome.

The cybersecurity world is debating WTF is going on with Bloomberg’s Chinese microchip stories • Motherboard

Jason Koebler, Joseph Cox, and Lorenzo Franceschi-Bicchierai:

»

On Tuesday, Bloomberg doubled down on its bombshell report from last week, which alleged China had surreptitiously implanted tiny chips into the motherboards of servers to spy on US companies such as Apple and Amazon. If true, this would be one of the worst hacks in history.

In its new story, Bloomberg reports that a US telecom discovered and removed “manipulated hardware” in its servers. The article does not name the telecom and the key claims are all attributed to one source, Yossi Appleboum, co-CEO of security consultant Sepio Systems. Bloomberg reports Appleboum provided “documents, analysis, and other evidence,” but does not publish those or provide more information about what types of documents or evidence it has.

It is not clear in the article that Bloomberg knows which telecom is apparently affected; it notes that Appleboum is covered by an non-disclosure agreement. Motherboard has reached out to 10 major US telecom providers, and the four biggest telecoms in the US have denied to Motherboard that they were attacked: In an email, T-Mobile denied being the one mentioned in the Bloomberg story. Sprint said in an email that the company does not use SuperMicro equipment, and an AT&T spokesperson said in an email that “these devices are not a part of our network, and we are not affected.” A Verizon spokesperson said: “Verizon’s network is not affected.” A CenturyLink spokesperson also denied that the company is the subject of Bloomberg’s new story.

«

The trio who wrote this are Motherboard’s security writers – and they’re probably three of the top five in the business.

Also telling: a Twitter thread by ex-NSA staffer Robert Lee, who says (inter alia) that the writers of the Bloomberg seem keen, and honest, but also attracted to conspiracy theories from anonymous sources.

As time goes by, the Bloomberg China microchip story is looking flakier.
link to this extract


Exclusive: iPad Pro Face ID details, 4K HDR video over USB-C, AirPods-like Apple Pencil 2 pairing, more • 9to5Mac

Guilherme Rambo:

»

Apple is widely expected to hold an event this month to introduce new 2018 iPad Pro models, new Macs, and more. Much of this has been confirmed by evidence within the iOS 12.1 beta, which includes references to an iPad2018Fall device.

Today, sources familiar with the development of the new 2018 iPad Pro have offered additional details about the device, its features, and more.

The model codes for the Wi-Fi models of the 2018 iPad Pro will be iPad8,1, iPad8,2, iPad8,5 and iPad8,6. Meanwhile, the cellular-capable models will be iPad8,3, iPad8,4 and iPad8,7 and iPad8,8.

This means there will be two Wi-Fi models in both size options, and two LTE models in both size options.

The new iPad Pros will have an edge-to-edge display and will not feature a Home button, much like the iPhone. Unlike the iPhone, however, the iPad Pro will not have a notch.

Even though the new 2018 iPad Pro models will sport thinner bezels, those bezels will still be wide enough to accommodate the TrueDepth camera system necessary for Face ID.

The 2018 iPad Pro will include Face ID with the same image signal processor as the iPhone XS, iPhone XS Max and iPhone XR. Further, we can confirm that Face ID on the new iPad Pro will work in both portrait and landscape orientations, though it won’t work upside down.

The Face ID setup process on the new iPad Pros will be very similar to the process introduced with the iPhone X. Notably, despite post-setup support for landscape Face ID, the setup process must be completed in portrait orientation.

It’s not clear if the new landscape support requires a special hardware feature, or if it can be made available to iPhones with a simple software update.

«

Including a thing called “iPad2018Fall” in your widely available beta is certainly a clever way to keep folk salivating. It does seem obvious that you’d be able to do FaceID in landscape: it’s just software correction.
link to this extract


Leaked transcript of private meeting contradicts Google’s official story on China • The Intercept

Ryan Gallagher:

»

[Ben] Gomes, [Google’s search engine chief] who joined Google in 1999 and is one of the key engineers behind the company’s search engine, said he hoped the censored Chinese version of the platform could be launched within six and nine months, but it could be sooner. “This is a world none of us have ever lived in before,” he said. “So I feel like we shouldn’t put too much definite into the timeline.”

It has been two months since The Intercept first revealed details about the censored search engine, code-named Dragonfly. Since then, the project has faced a wave of criticism from human rights groups, Google employees, U.S. senators, and even Vice President Mike Pence, who on Thursday last week called on Google to “immediately end development of the Dragonfly app that will strengthen the Communist Party’s censorship and compromise the privacy of Chinese customers.”

Google has refused to answer questions or concerns about Dragonfly. Earlier this month, a Google executive faced public questions on the censorship plan for the first time. Keith Enright told the Senate Commerce, Science and Transportation Committee that there “is a Project Dragonfly,” but said “we are not close to launching a product in China.” When pressed to give specific details, Enright refused, saying that he was “not clear on the contours of what is in scope or out of scope for that project.”

«

link to this extract


Google Call Screening: a personal robot that talks to, hangs up on spam calls • Ars Technica

Sam Machkovech:

»

Google Call Screening, which will debut on the new Pixel 3 and Pixel 3 XL phones in the US, has been announced as an “on-device” feature (as opposed to something driven by Duplex) that phone users can turn on when a phone call arrives from an unrecognized number. This will pick up the call and have a Google Assistant voice speak a prompt:

“Hi, the person you’re calling is using a screening service from Google, and will get a copy of this conversation. Go ahead and say your name, and why you are calling.”
Whatever the caller says in response will appear as a voice-to-text translation on the phone screen. At that point, Pixel phone users can elect to pick up the call, offer a robo-spoken response like “who is this?” or “I’ll call you back,” or mark the caller’s number as spam. In the demo’s case, the caller describes a contest for an “all-expenses paid trip to Hawaii.” The demo didn’t appear to offer any context-sensitive responses to the spam in question.

Google’s demo also didn’t include any out-loud sample of how calls between your phone’s Google Assistant voice and a robo-caller’s automated voice might sound. For now, the service doesn’t appear to offer the option to listen to the robot-on-robot action in question—in case, for example, you wanted to turn on a muted speakerphone while Google Call Screening did its thing. (We may want to hear the “conversation” in question, just to make sure Google’s promise of giving users a copy doesn’t quite turn out and that this isn’t a ploy to have spam-bots and Goog-bots join forces in a robo-revolution behind our backs.)

«

People I know in the US are being slowly driven mad by robocalls, especially to their mobiles. This is a super-smart move.

The rest of the Google Pixel 3 phone launch is pretty well covered in The Guardian.
link to this extract


More than one third of music consumers still pirate music • The Guardian

Laura Snapes and Ben Beaumont-Thomas:

»

More than one-third of global music listeners are still pirating music, according to a new report by the International Federation of the Phonographic Industry (IFPI). While the massive rise in legal streaming platforms such as Spotify, Apple Music and Tidal was thought to have stemmed illegal consumption, 38% of listeners continue to acquire music through illegal means.

The most popular form of copyright infringement is stream-ripping (32%): using easily available software to record the audio from sites like YouTube at a low-quality bit rate. Downloads through “cyberlocker” file hosting services or P2P software like BitTorrent came second (23%), with acquisition via search engines in third place (17%).

“Music piracy has disappeared from the media in the past few years but it certainly hasn’t gone away,” David Price, director of insight and analysis at IFPI, told the Guardian. “People still like free stuff, so it doesn’t surprise us that there are a lot of people engaged in this. And it’s relatively easy to pirate music, which is a difficult thing for us to say.”

«

I’m surprised by the size of this figure. The other day I was wondering whether anyone has had their internet access cut off under the UK’s Digital Economy Act, introduced in a rush in 2010, which has a “three strikes” rule. Maybe that’s worth looking into.

It’s mostly about “stream ripping” (to be able to listen to music offline, taken from a free streaming service), and search engines are still a culprit.

Also includes some interesting stuff about smart speaker listening.
link to this extract


Google Pixel Slate officially announced: here’s what you need to know • Android Authority

Andrew Grush:

»

It’s no secret the tablet market isn’t what it used to be. It’s hard to get excited about a tablet in 2018, but Google hopes to change that with its newly announced Google Pixel Slate.

The Google Pixel Slate is a Chrome OS-powered tablet that is also capable of transforming into a laptop using a keyboard dock. Essentially this is Google’s take on the Microsoft Surface.

There’s really only so many ways to design a tablet, and so there’s nothing particularly innovative to be seen here in terms of design. On the front sits a 12.3inch QHD LCD display with a 3:2 aspect ratio. You also get front-firing stereo speakers.

The Pixel Slate sports two 8 MP cameras, one above the display and the other in the top right corner of the tablet’s back. Using a tablet as a camera isn’t the most practical experience, though it’s certainly possible. Of course, the main purpose for the camera setup will be video calling.

At the top of the left edge, you will find a volume rocker, with a single USB-C port located near the bottom of the tablet. On the right edge of the Google Pixel Slate you’ll find a fingerprint scanner embedded into the power button. This is a first for Chrome OS devices.

«

Google makes a tablet. That’s brave. The thinking is more that it’s a ChromeOS thing, isn’t it.
link to this extract


Strategy Analytics: Mobile Advertising Spend Growth to Slow to 12% CAGR • Strategy Analytics Online Newsroom

»

After growing over 6-fold between 2013 and 2018, growth in mobile advertising revenue will fall to a 12% CAGR [compound annual growth rate] and the market value will reach $222bn in 2023. The mobile share of digital advertising will grow rapidly in less developed advertising markets but in advanced markets the share over mobile is reaching a plateau. Strategy Analytics expects mobile advertising to continue to suffer from headwinds including increased cautiousness following Facebook’s Cambridge Analytica scandal and the implementation of GDPR in 2018.

Mobile advertising will rise to 67% in 2023. In markets where multi-device use is high, like the U.S., mobile advertising will account for just 58% of all digital in 2023, while in mobile-centric markets like India it will reach 71%.

Asia-Pacific is leading the mobile transition, representing around 44% of global mobile ad spend across the period. At a country-level and in terms of absolute ad spend, the U.S., and mobile-first markets China and Japan will remain leaders although their positions will erode.

Search will remain the dominant mobile advertising format with 47% of ad spend across the period while mobile video ad spend will be the fastest growing (+16.5% CAGR over 2018-2023) driven by the adoption of 6-second mid-rolls, and vertical ad formats by industry leaders Snapchat, Facebook and more recently YouTube.

«

So it’s a sort of good-news-bad-news for Facebook (and properties) and Google (and properties).
link to this extract


Inside Apple’s war on iPhone fraud in China • The Information

Wayne Ma:

»

Five years ago, Apple was forced to temporarily close what was then its only retail store in Shenzhen, China, after it was besieged by lines of hundreds of customers waiting to swap broken iPhones for new devices, according to two former Apple employees who were briefed about the matter. In May 2013, the Shenzhen store logged more than 2,000 warranty claims a week, more than any other Apple retail store in the world, one of those people said.

After some investigation, Apple discovered the skyrocketing requests for replacements was due to a highly sophisticated fraud scheme run by organized teams. Rings of thieves were buying or stealing iPhones and removing valuable components like CPUs, screens and logic boards, replacing them with fake components or even chewing gum wrappers, more than a half-dozen former employees familiar with the fraud said. The thieves would then return the iPhones, claiming they were broken, and receive replacements they could then resell, according to three of those people. The stolen components, meanwhile, were used in refurbished iPhones sold in smaller cities across China, two of the people said…

…A turning point came in 2013, when an Apple data scientist discovered a way to measure the fraud by counting the number of iPhones that switched to new Apple IDs after the devices were replaced under warranty, the person said. Typically, a legitimate customer who gets a replacement logs into the new phone with their original Apple ID, which should match the broken iPhone that they returned to Apple, the person said.

But in fraud cases, replacement phones were usually registered with different Apple IDs because the devices immediately changed hands, the person said. The data scientist discovered more than 60% of replaced iPhones in China were getting new IDs, the person said.

Apple adopted the fraud methodology, known internally as Mismatch, and eventually had as many as 300 employees tackling the problem, which soon became material to the company, the person said.

«

This cost Apple billions. That’s quite some fraud ring there.
link to this extract


Google search losing some advertising business to Amazon, agencies say • CNBC

Michelle Castillo:

»

Amazon’s ad business is booming. Some advertisers are moving more than half of the budget they normally spend with Google search to Amazon ads instead, amounting to hundreds of millions of dollars, according to execs at multiple media agencies. Some of these execs requested anonymity as they are not authorized to discuss their clients’ expenditures in public.

Amazon’s growing success could pose a rare threat to Google parent company Alphabet, which generated $95.4bn in ad revenues last year, 86% of its total revenue. Google is the dominant digital advertising platform in the U.S., and will take in an estimated 37% of digital ad budgets in 2018. Although Alphabet does not disclose the breakdown of its ad revenue, most estimates believe the vast majority comes from search ads — approximately 83% in the year to date, according to research from eMarketer.

Alphabet has remained somewhat insulated from the threat so far, and its overall ad revenue growth actually accelerated in the first half of 2018 compared with last year. Not all categories of brands are shifting money to Amazon — most of the movement is coming in consumer packaged goods, while huge and lucrative advertising categories such as automotive and travel are not yet moving to Amazon. Also, while Google search may be flattening, advertisers are moving parts of their ad spend from other media to different Google properties, particularly YouTube.

«

The more things change, the more they stay the same.
link to this extract


The anatomy of a click: what happens to your data online • Huffington Post

James Ball:

»

You might have followed a link from social media, email, a search engine, or even just typed in a web address, but now you’ve arrived at a site your computer or phone has sent a message to its server asking it to deliver you the content you’ve asked for.

For any site showing programmatic adverts – including this one – this sets off a lengthy chain reaction. The first thing the site does is the obvious one that’s visible to us: it starts sending you the editorial (non-advertising) content that you’ve asked for. So far so good.

What it also does is then send a message saying – more or less – “give me some adverts please!” to a Supply Side Platform, a company specialised in doing the mirror of what the demand ones do: get as much info as it can to go into the matchmaking lottery and get the best price possible.

That Supply Side Platform then sends – via the website you visited – a request for your computer to send it as much information as it’s willing to: it will send details of your browser and its ID, your IP address (which gives your rough location), and as much information from cookies as it can, which can include details of your browsing history and much else.

Once it’s received whatever information your computer was willing to hand over – the more the better, as it lets advertisers target better – it bundles it up, and it’s ready for the main event: the auction for your attention.

«

Useful guide to what happens far, far faster than humans can imagine. One to refer to for the future.
link to this extract


You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

Errata, corrigenda and ai no corrida: none notified

Start Up No.926: the climate change deadline, Facebook gets visual, the GRU’s hasty fumbling, archiving the internet, and more


Google is about to be minus Google Plus. Photo by dolphinsdock on Flickr.

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

A selection of 11 links for you. Use them wisely. I’m @charlesarthur on Twitter. Observations and links welcome.

We have 12 years to limit climate change catastrophe, warns UN • The Guardian

Jonathan Watts:

»

The authors of the landmark report by the UN Intergovernmental Panel on Climate Change (IPCC) released on Monday say urgent and unprecedented changes are needed to reach the target, which they say is affordable and feasible although it lies at the most ambitious end of the Paris agreement pledge to keep temperatures between 1.5C and 2C.

The half-degree difference could also prevent corals from being completely eradicated and ease pressure on the Arctic, according to the 1.5C study, which was launched after approval at a final plenary of all 195 countries in Incheon in South Korea that saw delegates hugging one another, with some in tears.

“It’s a line in the sand and what it says to our species is that this is the moment and we must act now,” said Debra Roberts, a co-chair of the working group on impacts. “This is the largest clarion bell from the science community and I hope it mobilises people and dents the mood of complacency.”

Policymakers commissioned the report at the Paris climate talks in 2016, but since then the gap between science and politics has widened. Donald Trump has promised to withdraw the US – the world’s biggest source of historical emissions – from the accord. The first round of Brazil’s presidential election on Sunday put Jair Bolsonaro into a strong position to carry out his threat to do the same and also open the Amazon rainforest to agribusiness.

The world is currently 1C warmer than preindustrial levels. Following devastating hurricanes in the US, record droughts in Cape Town and forest fires in the Arctic, the IPCC makes clear that climate change is already happening, upgraded its risk warning from previous reports, and warned that every fraction of additional warming would worsen the impact.

«

Two things you can do immediately: stop eating meat (means less methane, and less deforestation, and less intensive land use); change to a green energy supplier. Also, insulate your home.
link to this extract


Is Putin’s power wavering? What the GRU spy story says • Medium

Rudolf Van Der Berg:

»

hacking the OPCW was strategically completely unimportant to Russia. Yes, the Skripal poisoning and the Chemical Warfare in Syria cases were investigated, but all the fingers had already pointed to Russia. Russia knew it had done both things. All they would figure out is that the OPCW is competent at its job and found traces of Russia’s wrong doing. Of course spies want to know everything, for example the (confidential) sources of data. However why this warranted an attack on such short notice, with such great risk is unclear. When you already know the answer to the question of the researchers and the timing of publication is quite clear, why send four guys with haste and diplomatic passports? It is so undiplomatic. To me it shows the clique around Putin is extremely unsure about themselves and their position. They need to know ahead what the outcome of the OPCW research is, otherwise they fear for their position.

The WADA/IOC hacking shows some spy tradecraft and to some extent it is understable, that Russia wants to know which delegates compromised themselves while online at these events. It may help Russia’s case (and it appears it did, as Russia can play again) However, you also have to wonder why this is a case for high ranking hackers from the most serious Russian intelligence agency. I mean, stealing the plans of a new USA missile seems a far better use of military intelligence. Really this is what you spent your time on? Why? It shows the insecurities of Russian leaders.

«

The comical nature of the GRU’s attempts to hack the OPCW, and the public shaming meted out by the Dutch and British intelligence services, must have hurt. But this is payback for years of interference abroad.
link to this extract


Google exposed user data, feared repercussions of disclosing to public • WSJ

Douglas MacMillan and Robert McMillan:

»

Google exposed the private data of hundreds of thousands of users of the Google+ social network and then opted not to disclose the issue this past spring, in part because of fears that doing so would draw regulatory scrutiny and cause reputational damage, according to people briefed on the incident and documents reviewed by The Wall Street Journal.

As part of its response to the incident, the Alphabet unit plans to announce a sweeping set of data privacy measures that include permanently shutting down all consumer functionality of Google+, the people said. The move effectively puts the final nail in the coffin of a product that was launched in 2011 to challenge Facebook and is widely seen as one of Google’s biggest failures.

A software glitch in the social site gave outside developers potential access to private Google+ profile data between 2015 and March 2018, when internal investigators discovered and fixed the issue, according to the documents and people briefed on the incident…

…In weighing whether to disclose the incident, the company considered “whether we could accurately identify the users to inform, whether there was any evidence of misuse, and whether there were any actions a developer or user could take in response,” [a Google spokesman] said. “None of these thresholds were met here.”

…The profile data that was exposed included full names, email addresses, birth dates, gender, profile photos, places lived, occupation and relationship status; it didn’t include phone numbers, email messages, timeline posts, direct messages or any other type of communication data, one of the people said.

«

That is a long time for “potential access”, which was via more than 130 APIs – masquerade as a developer and you’re in. The further one reads into this story the more astonishing it is.

Google subsequently published a blog post about how it’s closing down “consumer Google+” because, apparently, “there are significant challenges in creating and maintaining a successful Google+ product that meets consumers’ expectations.”

And for those of us who said Google+ was a flop, here’s what Google says today: “The consumer version of Google+ currently has low usage and engagement: 90% of Google+ user sessions are less than five seconds.” How many of those from people hitting the wrong button in GMail, I wonder?

But Google is still under a 20-year privacy oversight from the FTC, signed in 2011 after its disastrous Google Buzz experiment. The FTC must surely follow this up.
link to this extract


Google Pixel Slate: rumoured specs, features, leaks, price, release date • CNET

Justin Jaffe:

»

With one day to go until Google’s launch event scheduled for Oct. 9, we’ve heard just about every last detail about the company’s forthcoming Pixel and Pixel XL phones. And the rumors about a new convertible tablet also continue to pile up. 

The rumored Google Pixel Slate is said to include a front-facing and rear-facing camera with advanced camera technology, a fingerprint scanner and a new keyboard cover with a magnetic clasp and kickstand — similar to Microsoft’s Surface Pro, which was itself recently refreshed. 

The reports about the Chrome tablets have been preceded by an abundance of extensive, detailed information about Google’s rumored Pixel 3 and Pixel 3 XL — including photos and videos published by Russian bloggers and more photos and information gleaned from a Pixel 3 XL that was apparently left in the backseat of a Lyft. Google hasn’t confirmed anything about any of these reports about the phones or tablet.

But the company has invited media to an event in New York City on Oct. 9. In addition to introducing new tablets, new phones and perhaps other devices, Google is expected show off a new wireless charging stand and the latest version of its Android operating system, known as Android Pie, which features new AR capabilities and upgrades to its voice assistant. 

«

Well, zero days to go until the event. I’m also fairly confident Apple will release invitations to its October event for whatever, just to annoy Google a little. Unless it wants Google to stew in the Google+ fiasco just a little longer.

Nice timing on that one, Google, by the way.
link to this extract


High Court blocks Google iPhone privacy lawsuit • Computer Weekly

Lis Evenstad:

»

The lawsuit accused Google of unlawfully collecting personal information for profiling purposes for advertising by bypassing the default privacy settings that block user tracking on the iPhone’s Safari browser between August 2011 and February 2012, which contravenes data protection laws by taking personal information without consent, and sought compensation for up to £3.2bn.  

During the court hearing in May, lawyers for Google You Owe Us told the court that information collected by Google included race, physical and mental health, political leanings, sexuality, social class, financial, shopping habits, and location data

However, Justice Warby, who presided over the case, said today (8 October) in the judgment document, that he would not let the claim proceed because Lloyd, who led the claim, could not prove that himself “or any of those whom he represents have suffered “damage” within the meaning of the Data Protection Act”.

However, he added in a press summary that there was “no dispute that it is arguable that Google’s alleged role in the collection, collation and use of data obtained via the Safari Workaround was wrongful, and a breach of duty”.

«

This doesn’t quite make sense. In a previous incarnation of this case, about exactly the same infringement, we got this:

»

One of the issues was whether the breach of confidence and misuse of private information claims were “torts”. Tugendhat J said this of the approach: “Judges commonly adopt one or both of two approaches to resolving issues as to the meaning of a legal term, in this case the word “tort”. One approach is to look back to the history or evolution of the disputed term. The other is to look forward to the legislative purpose of the rule in which the disputed word appears”. Having looked to the history, he observed that “history does not determine identity. The fact that dogs evolved from wolves does not mean that dogs are wolves”.

The outcome (paragraphs 68-71): misuse of private information is a tort (and the oft-cited proposition that “the tort of invasion of privacy is unknown in English law” needs revisiting) but breach of confidence is not (given Kitetechnology BV v Unicor GmbH Plastmaschinen [1995] FSR 765).

«

The difference seems to be that the earlier case (which was resolved out of court before it went to the Supreme Court; plaintiffs prevailed in the High Court) wasn’t under the DPA. This one is.
link to this extract


Facebook launches Portal auto-zooming video chat screens for $199/$349 • Techcrunch

Josh Constine:

»

Today Facebook launches pre-sales of the $199 10in screen Portal, and $349 15.6in swiveling screen with hi-fi audio Portal , minus $100 if you buy any two. They’ve got “Hey Portal” voice navigation, Facebook Messenger for video calls with family, Spotify and Pandora for Bluetooth and voice-activated music, Facebook Watch and soon more video content providers, augmented reality Story Time for kids, a third-party app platform, and it becomes a smart photo/video frame when idle.

Knowing buyers might be creeped out, Facebook’s VP of Portal Rafa Camargo tells me “We had to build all the stacks — hardware, software, and AI from scratch — and it allowed us to build privacy into each one of these layers”. There’s no facial recognition and instead just a technology called 2D pose that runs locally on the device to track your position so the camera can follow you if you move around. A separate chip for local detection only activates Portal when it hears its wake word, it doesn’t save recordings, and the data connection is encrypted. And with a tap you can electronically disable the camera and mic, or slide the plastic privacy shield over the lens to blind it while keeping voice controls active.

«

“Knowing people might be creeped out” they built it for privacy. But then they connected it to Facebook. 🤔

Also: those are big screens (or the bigger one is). Clearly aimed at the kitchen.

My instinct: not going to be a hit.
link to this extract


The internet’s keepers? “some call us hoarders—I like to say we’re archivists” • Ars Technica

Nathan Mattise:

»

the Internet Archive offers much more than text these days. Its broadcast-news collection covers more than 1.6 million news programs with tools such as the ability to search for words in chyrons and access to recent news (broadcasts are embargoed for 24 hours and then delivered to visitors in searchable two-minute chunks). The growing audio and music portion of the Internet Archive covers radio news, podcasting, and physical media (like a collection of 200,000 78s recently donated by the Boston Library). And as Ars has written about, the organization boasts an extensive classic video game collection that anyone can boot up in a browser-based emulator for research or leisure. Officially, that section involves 300,000-plus overall software titles, “so you can actually play Oregon Trail on an old Apple C computer through a browser right now—no advertising, no tracking users,” [Wayback Machine director for the Internet Archive, Mark] Graham says.

“Some might call us hoarders,” he says. “I like to say we’re archivists.”

In total, Graham says the Internet Archive adds four petabytes of information per year (that’s four million gigabytes, for context). The organization’s current data totals 22 petabytes—but the Internet Archive actually holds on to 44 petabytes worth. “Because we’re paranoid,” Graham says. “Machines can go down, and we have a reputation.” That NASA-ish ethos helped the non-profit once survive nearly $600,000 worth of fire damage—all without any archived data loss.

«

Search words in chyrons (the text that flows along the bottom of screens). Now there’s a thing. What if we just tried to tell the story of the world in chyrons? How would a day look?
link to this extract


Physics holds the key to performing the flipping water bottle trick • Ars Technica

Jennifer Ouellette:

»

Think of how ice skaters extend their arms and legs to slow down rotation coming out of jumps or spins. It’s the same principle: conservation of angular momentum. Once the bottle is set in motion, its angular momentum remains constant. But shifting how the mass inside (the water) is distributed increases the bottle’s rotational inertia (how much force is required to start or keep it moving). This slows down the bottle’s rotational speed.

Physicists from the University of Twente in the Netherlands decided to analyze the underlying physics [of flipping a half-full bottle of water so it lands upright] more thoroughly in a series of rigorous experiments and develop a theoretical model. For the first version of the experiment, they used a partially filled water bottle. For the second version, they reduced the variables from the large number of water molecules in the bottle to just two tennis balls in a cylindrical container.


Video stills showing the motion of two tennis balls in a can being flipped.
P.J. Dekker et al.

In both cases, their measurements clearly showed the dramatic decrease of the container’s rotational speed, resulting in a nearly vertical descent, so the bottle landed neatly and upright. Tracking the sloshing of the liquid and the changing positions of the tennis balls demonstrated the redistribution of mass, shifting the moment of inertia.

«

link to this extract


Viral “manspreading” video is staged Kremlin propaganda • EU vs Disinfo

»

The St. Petersburg-based online magazine Bumaga found and interviewed one of the men appearing in the recording, who said that he was paid for acting as a victim.

So, if the video is fiction, and if In The Now even openly states this – what is then the purpose of promoting the story to international audiences? What is in it for a Russian state media outlet?

The key to a possible answer is found in the reactions the video has been able to spur.

In the comments section on Facebook, users express outrage against the alleged feminist activist, often in strongly misogynic language, with this comment as the most popular, gathering by now more than 14,000 likes: “Robin Stedman: This is not a protest, it’s assault. Maybe someone should pour bleach water on her for sticking her breasts out. Same thing.”

In other words, the video stages extreme feminist activism and manages to provoke extreme anti-feminist reactions.

A central element in the modus operandi of the famous “troll factory” in St. Petersburg has been to promote not just one, but different and opposing extreme views.

During the American Presidential election campaign in 2016, the goal of the operation was to sow discord in the political system, and address divisive issues via groups and pages falsely claiming to represent US activists. Messaging was e.g. not only pro-Trump, but also protesting against Trump, all to drive in wedges.

An investigation from 2017 by the independent Russian news outlet RBC found that “Russian trolls posing as Americans made payments to genuine activists in the US to help fund protest movements on socially divisive issues”.

«

Russia is so much better at information warfare than the west, principally because the west (particularly in the US) makes a habit of standing around looking for fights to pick. Men v women? Democrats v Republicans? Star Wars done by George Lucas v Star Wars done post-George Lucas? All hills worth dying on, apparently.
link to this extract


Falsehoods programmers believe about time and time zones • Creative Deletion

:

»

• Every day has 24 hours
Counterexample: Because of daylight saving time (DST) some days could have 23 hours and some could have 25 hours. Or some other amount of hours – whole or not.

• OK, but every day without DST changes is 86400 (60 * 60 * 24) seconds long
Sometimes the UTC offset for a time zone is changed.

• … at least in UTC
Leap seconds cause some days to have an extra second. And theoretically there could be negative leap seconds. Although negative leap seconds have not happened yet because the rotation of the earth so far has been slower than UTC, as it were, and not faster.

• Week one of a year starts in January every year
January 1st is not always a Monday so some days of an ISO week will be in different years. Example: 2014 December 28th belongs to week 1 of 2015.

• If I know what time zone someone is in and they just tell me the date and local time, I can always use software to find out what time that is in UTC
If they are in the middle of changing from summertime to wintertime, the clock will be set back one hour. This means that an hour exists twice, so to speak. If the clock is set back to 2:00 and someone tells you that the local time was 2:17 for instance, you do not know if he is talking about 2:17 before the clocks were set back or 2:17 after the clocks were set back.

«

And many more. (Thanks @stormyparis for the link.)
link to this extract


Geospatial Commission earmarks first investments • UK Authority

»

The Geospatial Commission has announced its first investments with plans to pump £5m into unlocking data held by the British Geological Survey, Coal Authority, HM Land Registry, Ordnance Survey, UK Hydrographic Office and the Valuation Office Agency.

The recently created organisation indicated it will provide £80m over the next two years to support the development of new products that can propel “British companies onto a global market”. 

The six to receive the first round of investments are the partner bodies of the commission, set up by the chancellor a year ago to exploit location information, or geospatial data.

Using this publicly held data more productively could be worth up to £11bn to the economy every year, the Government believes.

The data has been produced from delivering public services and enforcing laws – such as navigating public transport or tracking supply chains – but will now be analysed by private firms for new services.

David Lidington, the Cabinet Office minister, said: “This Government is committed to providing more opportunities for tech businesses – including small firms – to thrive, as well as access public procurement opportunities.”

«

That’s good – considering it took four years of lobbying, starting back in 2006, to get the government even to countenance making OS and UKHO data open, this is a continuation down a long road.
link to this extract


Errata, corrigenda and ai no corrida: none notified

Start Up No.925: more on SuperMicro, Windows rollout halted, Apple’s non-killing kill switch, Wikipedia bans Breitbart, and more

Monster’s founder and CEO in happier times – 11 years ago. Now things are much worse. Photo by giiks on Flickr.

»You can sign up to receive each day’s Start Up post by email (arriving at about 0700GMT each weekday). You’ll need to click a confirmation link, so no spam.«

A selection of 11 links for you. 3G and two bars will do. I’m @charlesarthur on Twitter. Observations and links welcome.

How Russian spies infiltrated hotel Wi-Fi to hack victims up close • Wired

Andy Greenberg:

»

some of the most surprising elements of those intrusion operations are the ones that got the Russian hackers caught red-handed: Parking vehicles outside of target buildings, and infiltrating Wi-Fi networks to hack victims.

“When the conspirators’ remote hacking efforts failed to capture log-in credentials, or if those accounts that were successfully compromised did not have the necessary access privileges for the sought-after information, teams of GRU intelligence officers traveled to locations around the world where targets were physically located,” the Justice Department’s indictment reads. “Using specialized equipment, and with the remote support of conspirators in Russia, these on-site teams hacked into Wi-Fi networks used by victim organizations or their personnel, including hotel Wi-Fi networks.”

The new details on those in-person hacking operations illustrate just how brash the GRU’s hackers have become, says John Hultquist, the director of research at security intelligence firm FireEye, who has closely tracked GRU operations for years. “If they’re willing to play like this, they are extremely aggressive,” Hultquist says. “It’s risky and brazen that they’re doing this physically. Obviously your chance of getting caught and exposed in person are higher, but it gives them a whole new avenue to get into networks that might have otherwise been a challenge.”

«

“Honey? Should I join this network called DEFINITELY NOT STEAL UR DATA? It doesn’t need a password.”
link to this extract


The untold story of Stripe, the secretive $20bn startup driving Apple, Amazon and Facebook • Wired

Stephen Armstrong:

»

Over the past year, 65% of UK internet users and 80% of US users have bought something from a Stripe-powered business, although very few of them knew they were using it. Where PayPal injects itself into the checkout process, Stripe operates like a white-label merchant account, processing payments, checking for fraud and taking a small percentage: 1.4% plus 20 pence for European cards and 2.9% plus 20 pence for all others. The buyer sees the seller’s name on their credit card statement and, unless the merchant specifically chooses to deploy the Stripe logo, that’s all they’ll ever see.

“It’s not the cheapest provider but it does remove all other intermediaries so it’s the only fee you’ll pay,” Hodges explains. “And if that’s all they did, they’d be interesting. It’s what they did next that’s revolutionary.”

“For many years Stripe had been trying to work out how to deal with what seemed like an obvious opportunity,” explains Billy Alvarado, Stripe’s chief business officer. Alvarado grew up in Honduras, where, in 1998, Hurricane Mitch took out all three bridges in the capital city. “Suddenly you had men, women and children, literally in rubber boots with these pads on their shoulders selling piggy backs across the river to men in suits and women in work clothes,” he recalls. “If you go to any country, you see entrepreneurship everywhere. A lot of these entrepreneurs would love to launch a global internet business. They find it difficult to trade on the world market – but these are literally millions of nascent businesses. We were just trying to work out how we can help them do that simply.”

On February 24, 2016 the company launched the Stripe Atlas platform, designed to help entrepreneurs start a business from absolutely anywhere on the planet. The invitation-only platform allows companies from the Gaza Strip to Berwick-upon-Tweed to incorporate as a US company in Delaware – a state with such business-friendly courts, tax system, laws and policies that 60% of Fortune 500 companies including the Bank of America, Google and Coca-Cola are incorporated there for just $500.

«

Would be great if Delaware would also reform itself so that you could trace ownership of businesses registered there, and bring dirty money to account. Hardly Stripe’s fault it would use it, though.
link to this extract


Some Apple Watch Series 4 models repeatedly crashing and rebooting due to daylight saving time bug • 9to5Mac

Benjamin Mayo:

»

A bug with the complications on the new Infograph faces in Apple Watch Series 4 is causing some very unhappy Watch owners today. Users in Australia have just experienced the daylight saving time change and are finding their Watches are now stuck in reboot loops.

Specifically, it seems the large Activity complication on the Infograph Modular face is not handling the loss of an hour elegantly, and instead causing the entire device to crash and reboot …

The Activity complication on the Infograph Modular face draws a timeline graph of the current day, showing hour-by-hour data for Move calories, Exercise minutes, and Stand Hours that make up the Activity rings.

In a typical day, there are obviously 24 hours. Although the exact problem has not yet been diagnosed, it appears that the large Activity complication simply cannot handle drawing its graph with one of those twenty four hour missing.

«

It would be hard to think of something guaranteed to throw off computers than daylight saving time.
link to this extract


Apple insiders say nobody internally knows what’s going on with Bloomberg’s China hack story • Buzzfeed News

John Paczkowski:

»

Reached by BuzzFeed News, multiple Apple sources — three of them very senior executives who work on the security and legal teams — said that they are at a loss as to how to explain the allegations. These people described a massive, granular, and siloed investigation into not just the claims made in the story, but into unrelated incidents that might have inspired them.

“We tried to figure out if there was anything, anything, that transpired that’s even remotely close to this,” a senior Apple security executive told BuzzFeed News. “We found nothing.”

A senior security engineer directly involved in Apple’s internal investigation described it as “endoscopic,” noting they had never seen a chip like the one described in the story, let alone found one. “I don’t know if something like this even exists,” this person said, noting that Apple was not provided with a malicious chip or motherboard to examine. “We were given nothing. No hardware. No chips. No emails.”

Equally puzzling to Apple execs is the assertion that it was party to an FBI investigation — Bloomberg wrote that Apple “reported the incident to the FBI.” A senior Apple legal official told BuzzFeed News the company had not contacted the FBI, nor had it been contacted by the FBI, the CIA, the NSA, or any government agency in regards to the incidents described in the Bloomberg report. This person’s purview and responsibilities are of such a high level that it’s unlikely they would not have been aware of government outreach.

«

Apple has been very firm in denying all this, as has Amazon. Quite where this goes next – lawsuits? – is unclear.
link to this extract


Apple’s secret repair kill switch hasn’t been activated—yet • iFixit

Adam O’Camb:

»

Apple’s [Mac repair] bulletin states that repairs to a laptop’s display assembly, logic board, upper case, and Touch ID board will require Apple’s secret software toolkit. In case you weren’t counting, that’s pretty much everything but the battery. On desktops, the logic board and flash storage are affected. But how?

Here’s how Apple describes the new process: After replacing a part, a technician must run the configuration suite, which connects to Apple’s Global Service Exchange (GSX) server to perform performance and compatibility checks for the new parts. Without this software, an internet connection, and approval from Apple’s servers, the repair is considered incomplete and the computer is rendered inoperative.

AST 2 is only provided to Apple stores and a very few select ‘Authorized Apple Service Providers’ (AASPs) that are under strict confidentiality and business contracts mandating what parts they can use and what they charge. This shift will leave third-party repair shops out to dry, not to mention the rest of us that are accustomed to fixing our own hardware. It is unclear whether this software is available to certified self-servicing accounts—if not, schools and businesses are out of luck too.

This service document certainly paints a grim picture, but ever the optimists, we headed down to our friendly local Apple Store and bought a brand new 2018 13” MacBook Pro Touch Bar unit. Then we disassembled it and traded displays with our teardown unit from this summer. To our surprise, the displays and MacBooks functioned normally in every combination we tried. We also updated to Mojave and swapped logic boards with the same results.

That’s a promising sign, and it means the sky isn’t quite falling—yet. But as we’ve learned, nothing is certain.

«

There’s a lot of noise about supply chain infiltration recently. I wonder if anyone at iFixit has considered that this might be Apple looking to offer customers protection against (1) counterfeit items (2) surveillance items and (3) people trying to hook covertly into the Secure Enclave? That was what Error 53 was about too. Apple is nothing if not consistent.
link to this extract


Microsoft pulls Windows 10 October 2018 update after reports of documents being deleted • The Verge

Tom Warren:

»

Microsoft is now recommending that affected users contact the company directly, and if you’ve manually downloaded the October update then “please don’t install it and wait until new media is available.” Other Windows 10 users have been complaining that the Microsoft Edge browser and other store apps have been unable to connect to the internet after the October 2018 Update, and the update was even blocked on certain PCs due to Intel driver incompatibilities.

It’s not clear how many Windows 10 users are affected by the problem, but even if it’s a small percentage it’s still surprising this issue was never picked up during Microsoft’s vast testing of the October update. Millions of people help Microsoft test Windows 10, but the company has struggled with the quality of Windows updates recently. Microsoft delayed its Windows 10 April 2018 Update earlier this year over Blue Screen of Death issues, but those problems were picked up before the update reached regular consumers and businesses.

Microsoft was planning to push the latest October update out to all Windows 10 users next Tuesday, but that’s now likely to be put on hold while investigations continue into this major deletion problem.

«

Warren pointed out on Twitter that Microsoft had been warned about this via the Windows Insider program, yet seems to have thought it fixed.
link to this extract


Making sense of the SuperMicro motherboard attack • Light Blue Touchpaper

Theo Markettos, who is on the security team at Cambridge University’s Computer Lab, considers whether what’s described in the attack is feasible:

»

there’s another trick a bad BMC can do — it can simply read and write main memory once the machine is booted. The BMC is well-placed to do this, sitting on the PCI Express interconnect since it implements a basic graphics card. This means it potentially has access to large parts of system memory, and so all the data that might be stored on the server. Since the BMC also has access to the network, it’s feasible to exfiltrate that data over the Internet.

So this raises a critical question: how well is the BMC firmware defended? The BMC firmware download contains raw ARM code, and is exactly 32MiB in size. 32MiB is a common size of an SPI flash chip, and suggests this firmware image is written directly to the SPI flash at manufacture without further processing. Additionally, there’s the OpenBMC open source project which supports the AST2400. From what I can find, installing OpenBMC on the AST2400 does not require any code signing or validation process, and so modifying the firmware (for good or ill) looks quite feasible.

Where does this leave us? There are few facts, and much supposition. However, the following scenario does seem to make sense. Let’s assume an implant was added to the motherboard at manufacture time. This needed modification of both the board design, and the robotic component installation process. It intercepts the SPI lines between the flash and the BMC controller. Unless the implant was designed with a very high technology, it may be enough to simply divert the boot process to fetch firmware over the network (either the Internet or a compromised server in the organisation), and all the complex attacks build from there — possibly using PCI Express and/or the BMC for exfiltration.

If the implant is less sophisticated than others have assumed, it may be feasible to block it by firewalling traffic from the BMC — but I can’t see many current owners of such a board wanting to take that risk.

So, finally, what do we learn? In essence, this story seems to pass the sniff test.

«

A change in the code (even later reversed) would show up in the repository, surely? Notable, though, that technical people think this attack entirely feasible.
link to this extract


Supply chain security is the whole enchilada, but who’s willing to pay for it? • Krebs On Security

Brian Krebs:

»

Most of what I have to share here is based on conversations with some clueful people over the years who would probably find themselves confined to a tiny, windowless room for an extended period if their names or quotes ever showed up in a story like this, so I will tread carefully around this subject.

The U.S. Government isn’t eager to admit it, but there has long been an unofficial inventory of tech components and vendors that are forbidden to buy from if you’re in charge of procuring products or services on behalf of the U.S. Government. Call it the “brown list, “black list,” “entity list” or what have you, but it’s basically an indelible index of companies that are on the permanent Shit List of Uncle Sam for having been caught pulling some kind of supply chain shenanigans.

More than a decade ago when I was a reporter with The Washington Post, I heard from an extremely well-placed source that one Chinese tech company had made it onto Uncle Sam’s entity list because they sold a custom hardware component for many Internet-enabled printers that secretly made a copy of every document or image sent to the printer and forwarded that to a server allegedly controlled by hackers aligned with the Chinese government.

That example gives a whole new meaning to the term “supply chain,” doesn’t it? If Bloomberg’s reporting is accurate, that’s more or less what we’re dealing with here in Supermicro as well.

But here’s the thing: Even if you identify which technology vendors are guilty of supply-chain hacks, it can be difficult to enforce their banishment from the procurement chain. One reason is that it is often tough to tell from the brand name of a given gizmo who actually makes all the multifarious components that go into any one electronic device sold today.

«

link to this extract


Wikipedia bans right wing site Breitbart as a source for facts • Motherboard

Samantha Cole:

»

Wikipedia editors voted to ban Breitbart as a source of fact in it articles. The consensus, reached late last month, agreed that the outlet “should not be used, ever, as a reference for facts, due to its unreliability.” Wikipedia editors also decided that InfoWars is a “conspiracy theorist and fake news website,” and that the “use of InfoWars as a reference should be generally prohibited.

Breitbart, a far-right conservative media website, has come under scrutiny—such as when it vehemently supported Alabama politician and alleged pedophile Roy Moore, when it shilled for scam cryptocurrencies through its newsletter, or when it fueled racist narratives about black NFL players. Wikipedians decided that because fact checkers have found much of Breitbart’s coverage to be “misleading, false or both,” they won’t abide it as a source of fact anymore.

“We have something over 2,500 links to Breitbart, many of them as sources in articles,” the editor who nominated the rule wrote in the vote. “I think that Breitbart is not a reliable source […] It’s my view that we should not source anything to Breitbart other than strictly factual and uncontroversial facts about Breitbart on the articles related to Breitbart and its people.”

The ensuing discussion about whether Breitbart should be considered a factual source went on for dozens of comments, many of them impassioned. But, overwhelmingly, editors believed it should be banned except when used as a source to attribute opinions or relevant commentary. It has been “deprecated” for English articles, and will no longer be used as a reliable source for facts on the English version of the online encyclopedia.

«

Wikipedia: still better at this sort of thing than most of the internet (and many bits of media), and still largely immune from cat-and-laser pointer attempts to distract it.
link to this extract


The iPhone XS & XS Max review: unveiling the silicon secrets • Anandtech

Andrei Frumusanu:

»

Apple promised a significant performance improvement in iOS12, thanks to the way their new scheduler is accounting for the loads from individual tasks. The operating system’s kernel scheduler tracks execution time of threads, and aggregates this into an utilisation metric which is then used by for example the DVFS mechanism. The algorithm which decides on how this load is accounted over time is generally simple a software decision – and it can be tweaked and engineered to whatever a vendor sees fit.

Because iOS’s kernel is closed source, we’re can’t really see what the changes are, however we can measure their effects. A relatively simple way to do this is to track frequency over time in a workload from idle, to full performance. I did this on a set of iPhones ranging from the 6 to the X (and XS), before and after the iOS12 system update.

Starting off with the iPhone 6 with the A8 chipset, I had some odd results on iOS11 as the scaling behaviour from idle to full performance was quite unusual. I repeated this a few times yet it still came up with the same results. The A8’s CPU’s idled at 400MHz, and remained here for 110ms until it jumped to 600MHz and then again 10ms later went on to the full 1400MHz of the cores.

iOS12 showcased a more step-wise behaviour, scaling up earlier and also reaching full performance after 90ms.

The iPhone 6S had a significantly different scaling behaviour on iOS11, and the A9 chip’s DVFS was insanely slow. Here it took a total of 435ms for the CPU to reach its maximum frequency. With the iOS12 update, this time has been massively slashed down to 80ms, giving a great boost to performance in shorter interactive workloads.

«

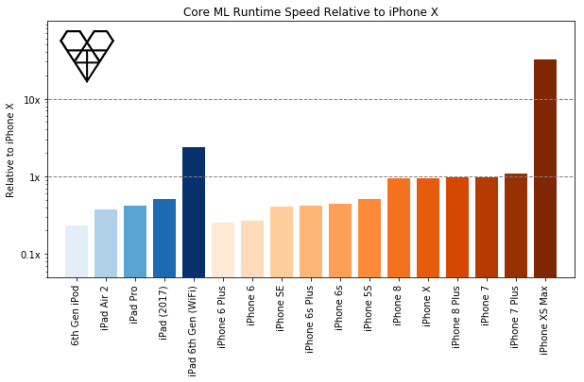
Most of this multi-page review is just benchmark gobbledygook to me, but this page and those graphics really stand out because it shows iOS 12 getting performance improvements of as much as 50% on old hardware, through tweaks to the core OS.
link to this extract


A Monster fall: how the company behind Beats lost its way • SF Chronicle

Melia Russell:

»

There was a time, not long ago, when Monster was on everyone’s ears. From 2009 to 2012, its sales of headphones, audio equipment and cables grew tenfold. That year, the company sold a billion dollars of gear, including the hit Beats brand. CEO Noel Lee hung out with music royalty like Lady Gaga and Mary J. Blige.

Now Monster is ailing, as is Lee, amid a fight with a former executive. Its sales have plummeted nearly 95% in five years. Retail stores such as Circuit City and RadioShack that once sold its wares have gone belly-up. Its partnership with Beats dissolved before the headphone maker saw a $3.2bn payday in its sale to Apple. A February Super Bowl ad, the company’s first ever, was a dud, with Marketing Week rating it a “loser.” And new ventures into online gambling and cryptocurrency have gone nowhere.

A company that once hung its name on San Francisco’s Candlestick Park is fighting for its life. While Lee proclaims that the company he founded four decades ago will see another 40 years, the company started laying people off in September.

Its South San Francisco headquarters now occupy just part of one floor of an office building. It shut a distribution center in Las Vegas late last year. In May, it reported having 139 employees, down from 800 a decade ago; the company won’t say how many remain.

«

Amazing; it relied on retail outlets for its products (which always promised far more than they could offer). That 95% fall in sales, though? They should be paired with HTC – which was also involved in Beats’s early years.
link to this extract


Errata, corrigenda and ai no corrida: none notified.

Start Up No.924: Google secures protesters, Microsoft ❤️ Android, Russia’s long troll game, Fitbit solves murder?, and more


“OK, get searching.” A Supermicro server, opened up. Photo by Patrick Finnegan on Flickr.

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

A selection of 11 links for you. Today’s forecast: cyber on a number of fronts. I’m @charlesarthur on Twitter. Observations and links welcome.

The big hack: how China used a tiny chip to infiltrate US companies • Bloomberg

Jordan Robertson and Michael Riley:

»

To help with due diligence, AWS, which was overseeing the prospective acquisition, hired a third-party company to scrutinize Elemental’s security, according to one person familiar with the process. The first pass uncovered troubling issues, prompting AWS to take a closer look at Elemental’s main product: the expensive servers that customers installed in their networks to handle the video compression. These servers were assembled for Elemental by Super Micro Computer Inc., a San Jose-based company (commonly known as Supermicro) that’s also one of the world’s biggest suppliers of server motherboards, the fiberglass-mounted clusters of chips and capacitors that act as the neurons of data centers large and small. In late spring of 2015, Elemental’s staff boxed up several servers and sent them to Ontario, Canada, for the third-party security company to test, the person says.

Nested on the servers’ motherboards, the testers found a tiny microchip, not much bigger than a grain of rice, that wasn’t part of the boards’ original design. Amazon reported the discovery to US authorities, sending a shudder through the intelligence community.

«

(The chips, they say, were put there by agents of the Chinese Peoples’ Liberation Army to spy on Amazon, Apple and others.)

This story has of course been cannoning around the internet, eliciting various gasps of amazement. Amazon and Apple have vehemently denied pretty much every element of the story, but the US government has been silent.

A few possibilities. 1) Apple and Amazon aren’t allowed to acknowledge it; it’s super-high security.
2) didn’t happen; it’s a ploy by US security to get manufacture brought back to the US because they’re worried about security of Chinese manufacture. (It’s not just a Trump-era ploy, because the reporters have been talking to their sources for years.)
3) everyone’s getting overheated – the chips weren’t what they’re being made out to be, which means it’s a version of No.2. Read the denials, though. Wow. Apple put out an even more aggressive denial, saying it’s not under any confidentiality demands.

One notable opinion is that this torpedoes China’s ambitions to supply chips: that nobody will trust them. I’d agree.
link to this extract


Google tested this security app with activists in Venezuela. Now you can use it too • CNET

Alfred Ng:

»

When connections aren’t secure, attackers can intercept DNS traffic, directing people to pages infected with malware instead, or completely block out online resources. Venezuela’s government has been known block access to social media applications and news websites through DNS manipulation, according to a study from the Open Observatory of Network Interference.

The practice is widespread, as researchers have found governments in more than 60 countries, including Iran, China and Turkey, using DNS manipulation to censor parts of the internet.

Intra was released on the Play Store on Wednesday morning for free, and Jigsaw had been testing its security features among a small group of activists in Venezuela since the beginning of the summer, Henck said.

They wanted to keep its public beta limited, but the app spread through word of mouth in Venezuela, to the point where activists from around the world started using it.

“People found it useful as a tool they could use to get the access that they needed,” Henck said.

Intra automatically points your device to Google’s public DNS server, but you’re able to point it to change it to other servers like Cloudflare’s 1.1.1.1 through the settings. There’s not much you need to do with it for your encrypted connection — the app really has only one button that you tap to turn on.

This encrypted connection to DNS servers comes by default on the upcoming version of Android Pie, but Jigsaw’s developers realized that millions of people that don’t have the latest updates wouldn’t have that same protection. It’s important to consider when about 80% of Android’s users aren’t on the latest version of the mobile operating system.

«

As long as you’re confident the Google Play link is safe.. But this is definitely a good thing.
link to this extract


Microsoft is embracing Android as the mobile version of Windows • The Verge

Tom Warren:

»

Android app mirroring will be part of Microsoft’s new Your Phone app for Windows 10. This app debuts this week as part of the Windows 10 October 2018 Update, but the app mirroring part won’t likely appear until next year. Microsoft briefly demonstrated how it will work, though; You’ll be able to simply mirror your phone screen straight onto Windows 10 through the Your Phone app, which will have a list of your Android apps. You can tap to access them and have them appear in the remote session of your phone.

We’ve seen a variety of ways of bringing Android apps to Windows in recent years, including Bluestacks and even Dell’s Mobile Connect software. This app mirroring is certainly easier to do with Android, as it’s less restricted than iOS. Still, Microsoft’s welcoming embrace of Android in Windows 10 with this app mirroring is just the latest in a number of steps the company has taken recently to really help align Android as the mobile equivalent of Windows.

Microsoft Launcher is designed to replace the default Google experience on Android phones, and bring Microsoft’s own services and Office connectivity to the home screen. It’s a popular launcher that Microsoft keeps updating, and it’s even getting support for the Windows 10 Timeline feature that lets you resume apps and sites across devices.

All of this just reminds me of Windows Phone.

«

Yeah, Tom, let it go now. But Microsoft trying to ju-jitsu Android by getting Windows connectivity? Seems smart.
link to this extract


Oppo, Vivo and Xiaomi top customer satisfaction in India • Strategy Analytics

»

Based on analysis of more than 20,000 consumer ratings and reviews of 11 high, mid and low-tier smartphones in the Indian market, Strategy Analytics’ new Consumer Ratings Index Report, India Smartphones: August 2018, has identified that Oppo’s Realme 1 led consumer satisfaction in India from June to August 2018.

• Based on consumer satisfaction, the top three smartphones in India from June to August 2018 were from Chinese brands: Oppo Realme 1, Vivo V9 and Xiaomi Redmi 5. Samsung’s Galaxy J8 was rated fourth.
• Consumer reviews in India mentioned the camera most. In fact, the Samsung Galaxy J8 and Vivo V9 were rated highest for camera satisfaction among those reviews analyzed.
• The Indian brand Karbonn was rated least favorably by Indian consumers, between June and August 2018.

Adam Thorwart, Lead Analyst and report author commented, “Despite Samsung not finishing atop the consumer sentiment chart, consumers of other brands are still mentioning it most. In fact, it nearly triples Oppo which is the second most mentioned brand. This indicates that Samsung is still very popular across India.”

«

Chinese brands are six of the top 11 top-selling brands. It’s a conquest.
link to this extract


Reckless campaign of cyber attacks by Russian military intelligence service exposed • UK National Cyber Security Centre

»

Today, the UK and its allies can expose a campaign by the GRU, the Russian military intelligence service, of indiscriminate and reckless cyber attacks targeting political institutions, businesses, media and sport.

The National Cyber Security Centre (NCSC) has identified that a number of cyber actors widely known to have been conducting cyber attacks around the world are, in fact, the GRU.  These attacks have been conducted in flagrant violation of international law, have affected citizens in a large number of countries, including Russia, and have cost national economies millions of pounds.

Cyber attacks orchestrated by the GRU have attempted to undermine international sporting institution WADA, disrupt transport systems in Ukraine, destabilise democracies and target businesses.

This campaign by the GRU shows that it is working in secret to undermine international law and international institutions.

«

It then lists 10 attacks which it attributes to the GRU – “high confidence the GRU was almost certainly responsible”. Maybe just do a confidence score out of 10?
link to this extract


Russian trolls tweeted disinformation long before US election • WSJ

Rob Barry:

»

Alice Norton posted an emergency message on a cooking-website forum on Thanksgiving 2015: Her entire family had severe food poisoning after buying a turkey from Walmart.

“My son Robert got in the hospital and he’s still there,” wrote Ms. Norton, who had described herself as a 31-year-old New York City mother of two. “I don’t know what to do!”

Within hours, Twitter users repeated the claim thousands of times, and a news story was published saying 200 people were in critical condition after eating tainted turkey.

The catch? No outbreak of food poisoning matching this description occurred, according to New York City health officials. A Walmart Inc. spokesman said the company had spotted the posts but determined they were a hoax and didn’t investigate their origin further.

In fact, many of the claims came from accounts linked to a pro-Kremlin propaganda agency charged by Special Counsel Robert Mueller’s office last week for meddling in U.S. politics. Security experts now believe the early posts, and others like them, may have been practice for a bigger target: the 2016 U.S. election.

While it is impossible to be sure what was in the minds of Russians tweeting false stories in 2014 and 2015—which also included tales of contaminated water, terrorist attacks and a chemical-plant explosion—these experts say it is as if the Russians were testing to see how much they could get Americans to believe.

«

Turns out that the latter is “really quite a lot”. America’s a big country, and a lot can happen. And a lie can get halfway around the world before the truth has got its boots on, as people say.
link to this extract


Smaller outlets reduce, scrap Facebook promotion over new ad rules • Columbia Journalism Review

Mathew Ingram:

»

To promote political news stories, Facebook requires that publishers apply and be authorized as a political advertiser—presumably to prove that they aren’t a front for a Russian or Iranian troll factory. The process requires the uploading of official ID, such as a driver’s license, a passport, or the last four digits of a Social Security Number, along with receipt of a registered letter at an approved US address.

For larger media outlets, these requirements might be complicated and annoying. For smaller publishers, Facebook’s new rules can be so unwieldy and demanding—and the definition of what constitutes a “political news story” so capricious—that small newsrooms in four states told CJR they are either scaling back their Facebook usage or, in some cases, have given up on promoting their content there at all.

Nick Kratsas, the digital operations director for southwestern Pennsylvania’s Observer-Reporter, went through Facebook’s approval process in order to promote his site’s political stories; he says his company gets a significant amount of traffic and engagement from the social network. About 55% of its monthly visits are due to Facebook links. (Like many other publishers, the paper has seen a drop after the latest algorithm changes, a decline that Kratsas recently estimated at about 8 percent.)

Kratsas says the platform’s tendency to flag any news story that mentions a politician or political topic has become so irritating that he wonders whether it is really worth the time that his company spends on it. The rest of the Observer-Reporter team hasn’t gone through Facebook’s authorization process, says Kratsas, and they are still finding their stories denied for allegedly political topics.

«

Unintended consequences: local news gets stuffed.
link to this extract


Police use Fitbit data to charge 90-year-old man in stepdaughter’s killing • The New York Times

Christine Hauser:

»

On Sept. 13, a co-worker of Ms. Navarra’s went to the house to check on her because she had not showed up for her job at a pharmacy, the report said. The front door was unlocked, and she discovered Ms. Navarra dead, slouched in a chair at her dining room table.

She had lacerations on her head and neck, and a large kitchen knife was in her right hand, the report said. Blood was spattered and uneaten pizza was strewn in the kitchen. The coroner ruled the death a homicide.

Detectives then questioned Ms. Navarra’s only known next-of-kin, her 92-year-old mother, Adele Aiello, and [stepfather] Mr. Aiello. Mr. Aiello told the authorities he had dropped off the food for his stepdaughter and left her house within 15 minutes, but he said he saw Ms. Navarra drive by his home with a passenger in the car later that afternoon.

Investigators obtained a search warrant and retrieved the Fitbit data [from Ms Navarra’s AltaHR worn on her wrist, which measured her heartbeat] with the help of the company’s director of brand protection, Jeff Bonham, the police report said…

When Ms. Navarra’s Fitbit data was compared with video surveillance from her home, the police report said, the police discovered that the car Mr. Aiello had driven was still there when her heart rate stopped being recorded by her Fitbit.

Bloodstained clothes were later found in Mr. Aiello’s home, the document said. He was arrested on Sept. 25.

«

When I was younger, some sci-fi stories had the idea of monitors which rich people wore to monitor their heartbeat, so that if they were killed, the killer wouldn’t get away. Turns out they’re available in your local store.
link to this extract


Artificial sweeteners are toxic to digestive gut bacteria: study • CNBC

Alexa Lardieri:

»

According to a study published in the journal Molecules, researchers found that six common artificial sweeteners approved by the Food and Drug Administration and 10 sport supplements that contained them were found to be toxic to the digestive gut microbes of mice.

Researchers from Ben-Gurion University of the Negev in Israel and Nanyang Technological University in Singapore tested the toxicity of aspartame, sucralose, saccharine, neotame, advantame, and acesulfame potassium-k. They observed that when exposed to only 1 milligram per milliliter of the artificial sweeteners, the bacteria found in the digestive system became toxic…

…According to the study, the gut microbial system “plays a key role in human metabolism,” and artificial sweeteners can “affect host health, such as inducing glucose intolerance.” Additionally, some of the effects of the new FDA-approved sweeteners, such as neotame, are still unknown.

«

Glucose intolerance.. which could be a step towards diabetes.
link to this extract


BlackBerry races ahead of security curve with quantum-resistant solution • TechCrunch

Ron Miller:

»

Today, BlackBerry announced a new quantum-resistant code signing service to help battle that possibility.

The service is meant to anticipate a problem that doesn’t exist yet. Perhaps that’s why BlackBerry hedged its bets in the announcement saying, “The new solution will allow software to be digitally signed using a scheme that will be hard to break with a quantum computer.” Until we have fully functioning quantum computers capable of breaking current encryption, we probably won’t know for sure if this works.

But give BlackBerry credit for getting ahead of the curve and trying to solve a problem that has concerned technologists as quantum computers begin to evolve…

…”If your product, whether it’s a car or critical piece of infrastructure, needs to be functional 10-15 years from now, you need to be concerned about quantum computing attacks,” Charles Eagan, BlackBerry’s chief technology officer, said in a statement.

«

I would like to announce that I have got software which will be hard to break by nine-legged aliens intent on dominating our planet. I thought it was important to get ahead of the curve and try to solve a problem that has concerned me since, well, yesterday.
link to this extract


The interesting ideas in Datasette • Simon Willison

The aforesaid Willison, who has built a database tool called Datasette which uses SQLite databases (caution: can only store up to 140TB – yes, terabytes). This will interest you if you’re into data tools; Willison built the tools that the Guardian used to analyse MPs’ expenses:

»

Since the data in a Datasette instance never changes, why not cache calls to it forever?

Datasette sends a far future HTTP cache expiry header with every API response. This means that browsers will only ever fetch data the first time a specific URL is accessed, and if you host Datasette behind a CDN such as Fastly or Cloudflare each unique API call will hit Datasette just once and then be cached essentially forever by the CDN.

This means it’s safe to deploy a JavaScript app using an inexpensively hosted Datasette-backed API to the front page of even a high traffic site—the CDN will easily take the load.

Zeit added Cloudflare to every deployment (even their free tier) back in July, so if you are hosted there you get this CDN benefit for free.

What if you re-publish an updated copy of your data? Datasette has that covered too. You may have noticed that every Datasette database gets a hashed suffix automatically when it is deployed:

https://fivethirtyeight.datasettes.com/fivethirtyeight-c9e67c4

This suffix is based on the SHA256 hash of the entire database file contents—so any change to the data will result in new URLs. If you query a previous suffix Datasette will notice and redirect you to the new one.

If you know you’ll be changing your data, you can build your application against the non-suffixed URL. This will not be cached and will always 302 redirect to the correct version (and these redirects are extremely fast).

https://fivethirtyeight.datasettes.com/fivethirtyeight/alcohol-consumption%2Fdrinks.json

The redirect sends an HTTP/2 push header such that if you are running behind a CDN that understands push (such as Cloudflare) your browser won’t have to make two requests to follow the redirect.

«

link to this extract


Errata, corrigenda and ai no corrida: none notified

Start Up No.923: the robot autonomous farm, Tim Cook on data, the information terrorists, XS camera in depth, and more


What if you could completely automate your job? Some people have. Photo by Brian J. Matis on Flickr.

A selection of 11 links for you. Use them wisely. I’m @charlesarthur on Twitter. Observations and links welcome.

How to program your job • The Atlantic

Brian Merchant:

»

It can seem that some of the only workers who have realized any scrap of that rusty old promise of automation are the ones who’ve carved out the code to claim it for themselves.

Programmers, of course, have been writing code that automates their work for decades. Programming generally involves utilizing tools that add automation at different levels, from code formatting to merging to different codebases—most just don’t take it to the extreme of fully or nearly fully automating their job. I chatted, via direct message on Reddit and email, with around a dozen programmers who said they had. These self-automators had tackled inventory management, report writing, graphics rendering, database administration, and data entry of every kind. One automated his wife’s entire workload, too. Most asked to remain anonymous, to protect their jobs and reputations.

“When I started, my job literally took me eight hours a day,” an early self-automator, who I’ll call Gary, told me. He worked for a large corporate hotel chain that was beginning to computerize its workflow in the ‘90s. Gary quickly recognized that he was spending a lot of his time repeating the same tasks, so he started learning to code after-hours. “Over the course of about three months, I built a piece of code in Lotus [1-2-3, then a popular PC spreadsheet program] that not only automated individual repetitive tasks, it effectively automated the entire job.” He didn’t tell his bosses exactly what he had done, and the quality of his working life improved considerably.

“It felt weird to have free time during the day,” he told me. “I spent that time learning about the other systems in the hotel.” He then made himself useful, helping management with bottlenecks in those systems.

«

What’s fascinating – even a little surprising – is how those who did this began to feel. They worried that they ought to be doing something, even though they were “doing” their job.
link to this extract


New autonomous farm wants to produce food without human workers • MIT Technology Review

Erin Winick:

»

As the firm’s cofounder Brandon Alexander puts it: “We are a farm and will always be a farm.”

But it’s no ordinary farm. For starters, the company’s 15 human employees share their work space with robots who quietly go about the business of tending rows and rows of leafy greens.

Today Iron Ox is opening its first production facility in San Carlos, near San Francisco. The 8,000-square-foot indoor hydroponic facility—which is attached to the startup’s offices—will be producing leafy greens at a rate of roughly 26,000 heads a year. That’s the production level of a typical outdoor farm that might be five times bigger. The opening is the next big step toward fulfilling the company’s grand vision: a fully autonomous farm where software and robotics fill the place of human agricultural workers, which are currently in short supply.

Iron Ox isn’t selling any of the food it produces just yet (it is still in talks with a number of local restaurants and grocers). So for now, those tens of thousands of heads of lettuce are going to a local food bank and to the company salad bar. Its employees had better love  eating lettuce.

The farm’s non-lettuce-consuming staff consists of a series of robotic arms and movers. The arms individually pluck the plants from their hydroponic trays and transfer them to new trays as they increase in size, maximizing their health and output—a luxury most outdoor farms don’t have. Big white mechanical movers carry the 800-pound water-filled trays around the facility.

«

Food is where technology got its big start. Thigh bones of antelopes, axes, knives, ploughs…
link to this extract


Apple CEO Tim Cook says giving up your data for better services is ‘a bunch of bunk’ • The Washington Post

Hamza Shaban:

»

Apple chief executive Tim Cook urged consumers not to believe the dominant tech industry narrative that the data collected about them will lead to better services.

In an interview with “Vice News Tonight” that aired Tuesday, Cook highlighted his company’s commitment to user privacy, positioning Apple’s business as one that stands apart from tech giants that compile massive amounts of personal data and sell the ability to target users through advertising.

“The narrative that some companies will try to get you to believe is: I’ve got to take all of our data to make my service better,” he said. “Well, don’t believe them. Whoever’s telling you that, it’s a bunch of bunk.”

Cook’s remarks come at a pivotal time for Silicon Valley. In the past year, technology companies and their executives have come under unprecedented scrutiny from elected officials and regulators stemming from a variety of issues, including a barrage of data privacy scandals, accusations of toxic corporate culture, the negative impact of tech platforms on political debate, and concerns over tech overuse and addiction. In recent months, growing calls from Capitol Hill have boosted the prospects of new legislation aimed at big tech companies…

…Cook said in the interview that he is “exceedingly optimistic” that the topic of data privacy has reached an elevated level of public debate. “When the free market doesn’t produce a result that’s great for society you have to ask yourself what do we need to do. And I think some level of government regulation is important to come out on that.”

«

link to this extract


Are smartphones the next generation consoles? • Strategy Analytics

»

By streaming games over networks, and invalidating the need for expensive hardware, game streaming services could potentially eliminate the concept of gaming generations by making any portable device a viable gaming machine. A new report from the User Experience Strategies (UXS) group at Strategy Analytics, Game Streaming: The Last Console Generation?, has assessed existing game streaming and download services to study the user experience issues that can arise from them. Streaming games over the internet could affect gaming in the same way that Netflix has affected video; but there are unique challenges that must be addressed for it to reach mainstream appeal.

Key report findings:

• Though game streaming could invalidate the need for bulky home consoles, proprietary controllers are still required. Since cross-platform games all feature different control schemes, the need for a universal standard is clear.
• It is nearly impossible to guarantee an ideal game streaming service for everyone, which is problematic when the service comes with a monthly charge. Factors like bandwidth and latency are key issues, but other interruptions to a service can affect the overall user experience.
• Games processed in the cloud are free from the limitations of hardware and could allow game developers to create experiences that would be otherwise impossible to achieve on aging hardware.

«

That need for proprietary controllers to get the best results is going to be a problem for their thesis.
link to this extract


FireEye unmasks a new North Korean threat group • Cyberscoop

Sean Lyngaas:

»

There is a distinct and aggressive group of hackers bent on financing the North Korean regime and responsible for millions of dollars in bank heists in recent years, according to research from cybersecurity company FireEye.

The group, dubbed APT38, is distinct from other Pyongyang-linked hackers because of its overriding financial motivation — as opposed to pure espionage — and persistent targeting of banks worldwide, FireEye researchers said.

“This is an active … threat against financial institutions all around the world,” Sandra Joyce, FireEye’s vice president of global intelligence, said at a press briefing.

The group was responsible for some of the more high-profile attacks on financial institutions in the last few years, the researchers said, including the $81m heist of the Bangladesh’s central bank in February 2016, and an attack on a Taiwanese bank in October 2017.

«

The Bangladesh bank one was widely known, but not the Taiwanese one. North Korea’s GDP is so tiny, and its foreign exchange reserves so tiny that this was a smart move.
link to this extract


Judge Kavanaugh and the information terrorists trying to reshape America • WIRED

Molly McKew:

»

In 2014, Chuck Johnson explained in a Mother Jones interview how he offered “bounties” to independent online researchers to solve “puzzles” that he gave them. What he said is actually a good description of why QAnon works: “You get all these hobbyists and amateurs and people out there who have a lot of time on their hands, many of whom are retired or they’re a mother, their kids are sleeping while they’re researching, they’re stay-at-home moms, or they’re college students or they’re unemployed or this is their moonlighting thing. All those people are starting to find one another.” It’s that sense of being a part of a bigger mission…

…even before Q was visible at Trump rallies and the media was writing about it, there was a disturbance in the Q-force. In May 2018, Infowars and the others in the Stone cadre started urgently denouncing QAnon, saying it had been “hijacked” by a deep-state information campaign or maybe just by people out to make a buck. For most of the summer, Posobiec teased that he would explain the whole deal.

In September, his opus supposedly debunking QAnon debuted, outing MicroChip, the aforementioned bot-king, and someone named Dreamcatcher as the creators of QAnon. According to Micro (if any of this is to be believed), they basically just created a word salad out of the stuff Trump supporters believed—the sex trafficking mania, Clinton is about to be arrested, the Generals, Russia’s not a thing, Trump is the savior—and made a list of questions that would tantalize that audience and engage them online.

“It was meant to be funny, to get people’s imaginations going,” Micro said in his interview with Posobiec. “It’s not supposed to go this far.” He said they only wrote a few of the original posts, essentially to bring disparate factions of the Trump movement together, and then someone else took it over.

«

Fascinating tour around the insane alt-right conspiracy theories. And their idiot helpers.
link to this extract


iPhone XS: why it’s a whole new camera • Halide

Sebastiaan de With:

»

After testing the iPhone XS side by side with the X, we found the XS prefers a faster shutter speed and higher ISO level. In other words, it takes photos a lot faster, but comes at the cost of noise.


iPhone X RAW on the left, iPhone XS RAW on the right. Note the increase in visible noise!

Two shots taken with the iPhone X (left) and iPhone XS (right). Taken in RAW so the extra noise can be seen—RAW on iPhone omits any noise-reduction steps. Why does the iPhone XS’ frame have to be noisier?

Remember that line-up of frames showing how the iPhone camera works?

Unless you have bionic arms, it’s impossible to hold your phone perfectly still for this long. To get a sharp, perfectly aligned burst of images, the iPhone needs to take photos really fast. That requires a shorter shutter speed — and that, in turn, means that there will be more noise in the image.
That noise has to be removed, somehow, and that comes at a cost: noise reduction removes a bit of detail and local contrast.


The iPhone XS RAW exposure on the left shows less ‘smoothed’ detail in the reflections, compared to its regular Smart HDR counterpart on the right.

«

There’s tons more: as you’d expect from people who developed a camera app. (Thanks @stormyparis for the link.)
link to this extract


Here come Wi-Fi 4, 5 and 6 in plan to simplify 802.11 networking names • CNet

Jessica Dolcourt:

»

Quick quiz: which is better, 802.11n or 802.11ac?

The answer, if you’re familiar with Wi-Fi standards coming from the Institute of Electrical and Electronics Engineers, is 802.11ac – and by the way, the upcoming 802.11ax is better than both.

But in an effort to make the wireless networking terms more useful and less like alphanumeric gibberish, the Wi-Fi Alliance trade group has some new names it wants for those technologies: Wi-Fi 4, Wi-Fi 5, and Wi-Fi 6.

The idea is to be clearer about what’s better and what your phone or home router can handle without sounding as much like an electronic engineer. Not that there’s anything wrong with electronic engineers, but even techies can have a hard time remembering that IEEE 802.11 means wireless networks, IEEE 1394 governs FireWire data connections, and IEEE 802.3 is about Ethernet network connections.

«

THANK. GOD. Also, will the numbers indicate maximum speeds somehow? Hmm, except Wi-Fi 1 (802.11b) would be Wi-Fi 11. Hmm.
link to this extract


Why you shouldn’t use Facebook to log in to other sites • NY Times

Farhad Manjoo:

»

neither Facebook nor third-party sites seem to know the precise extent of the damage. In a statement on Tuesday, Guy Rosen, Facebook’s vice president of product management, said the company had “no evidence” that attackers breached other sites through the hack, but that the company was building more sophisticated ways for sites to do their own deeper investigation.

But the mere possibility is highly troubling — and if the hack allowed access to any other sites, Facebook should be disqualified from acting as your sign-on service.

This is a classic you-had-one-job situation. Like a trusty superintendent in a Brooklyn walk-up, Facebook offered to carry keys for every lock online. The arrangement was convenient — the super was always right there, at the push of a button. It was also more secure than creating and remembering dozens of passwords for different sites. Facebook had a financial and reputational incentive to hire the best security people to protect your keys; tons of small sites online don’t — and if they got hacked and if you reused your passwords elsewhere, you were hosed.
ADVERTISEMENT
But the extensive hack vaporizes those arguments. If the entity with which you trusted your keys loses your keys, you take your keys elsewhere. And there are many more-secure and just-as-convenient ways to sign on to things online.

The best way is to use a dedicated password manager — a service, like LastPass or 1Password, that creates and remembers strong passwords for different sites. Operating systems and browsers are also getting better at managing passwords; newer iPhones, for instance, let you unlock sites with facial recognition, which is just as convenient as pressing Facebook’s button.

If for some reason you don’t want to use a password manager, you can use another tech giant’s sign-on service. When presented with different ways to sign on to sites, you can choose Google or Microsoft instead of Facebook.

«

Though what happens when those single sign-ons (SSOs) at Google or Microsoft get hacked? I did commission a piece at The Guardian back in 2010 or so from a US startup which found that teens didn’t like using Facebook to sign into a new app, because they didn’t feel it was anonymous – that Facebook would know what they were doing.
link to this extract


More than nine million broken links on Wikipedia are now rescued • Internet Archive

Mark Graham:

»

As part of the Internet Archive’s aim to build a better Web, we have been working to make the Web more reliable — and are pleased to announce that nine million formerly broken links on Wikipedia now work because they go to archived versions in the Wayback Machine.

For more than five years, the Internet Archive has been archiving nearly every URL referenced in close to 300 wikipedia sites as soon as those links are added or changed at the rate of about 20 million URLs/week.

And for the past three years, we have been running a software robot called IABot on 22 Wikipedia language editions looking for broken links (URLs that return a ‘404’, or ‘Page Not Found’). When broken links are discovered, IABot searches for archives in the Wayback Machine and other web archives to replace them with. Restoring links ensures Wikipedia remains accurate and verifiable and thus meets one of Wikipedia’s three core content policies: ‘Verifiability’.

To date we have successfully used IABot to edit and “fix” the URLs of nearly six million external references that would have otherwise returned a 404. In addition, members of the Wikipedia community have fixed more than six million links individually. Now more than nine million URLs, on 22 Wikipedia sites, point to archived resources from the Wayback Machine and other web archive providers.

«

This is impressive (and also means that at a stroke the Internet Archive has become the top destination for outgoing clicks from Wikipedia). Any time you want to give money for the IA’s work, feel free – don’t wait for my Christmas charity request.
link to this extract


Redesigning Siri and adding multitasking features to iOS • UX Design

Kévin Eugène:

»

I wanted to imagine an update that I would personally be excited about if it showed up at the WWDC, and this is what I came up with.

Let me introduce you to iOS Mogi.

This is Mogi, a beautiful fishing village near Nagasaki in Japan. I took this picture last year.

« Hey Siri, help me »
The first part of this concept is focused on Siri. The idea here is not to create new commands, rather to display existing vocal requests that work well (like « Find me a good restaurant nearby » or « Get me pictures of Japan I took last year ») in a different way so they could be more useful to the user.
In iOS Mogi, Siri has been designed around a concept I call parallel help. The idea is to have a vocal assistant that is non-intrusive (it won’t take the whole screen like it does today), context aware, and can do things in the background for the user while they are doing something else.
As images are more explicit than words, here’s a very simple example:

Using Siri in Messages.
When using apps, Siri takes the shape of a notification so as to be less intrusive as possible (if summoned from the lock screen or the home screen, it will still be fullscreen).

In the example above, I ask Siri to show me pictures of Japan as I want to send one to my friend Yannick. Once the request is fulfilled, the result is displayed in the Siri notification so I can continue to do what I was doing without being interrupted. I can swipe down the notification to reveal more and select the photos I want to send.

«

Like that? He’s only just getting started. The idea of Siri as a really helpful full-time assistant which you call on (rather than which prods you annoyingly, Clippy-style) is truly attractive.
link to this extract


Errata, corrigenda and ai no corrida: sorry about the spelling error yesterday.

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

Start Up No.922: how Tesco Bank was hacked, Microsoft’s black Surface, Amazon’s rippling pay rise, Trump’s tax fiddles, and more


Surprise! Over half the online complaints about this film came from bots and trolls. Photo by Brian Crawford on Flickr.

A selection of 9 links for you. Tax that return. I’m @charlesarthur on Twitter. Observations and links welcome.

Microsoft Surface Pro 6 announced with a new matte black finish, quad-core processors • The Verge

Tom Warren:

»

Microsoft’s Surface chief, Panos Panay, says the company has overhauled the inside of the Surface Pro 6 so it has improved cooling. That means the Surface Pro 6 now supports quad-core processors, and Microsoft claims it will be 67% faster than the previous model.

This new internal design should also help improve battery life. Microsoft says the Surface Pro 6 will last for 13.5 hours on battery life. While there’s an internal redesign, the outside looks very familiar. It’s still 1.7 pounds, and it has the same 12.3-inch display and up to 16GB of RAM inside.

Unfortunately, the Surface Pro 6 will include the same connectivity and external design as the existing model, which means there are still no USB-C ports. It’s surprising Microsoft still isn’t adopting USB-C in its flagship Surface Pro, especially given the company has introduced this new connector on both the Surface Go and Surface Book 2.

«

“Matte black finish” is the key point for the headline? And still USB-C can’t get any love.
link to this extract


Amazon’s $15-per-hour minimum wage will change how Americans see work • Bloomberg

Conor Sen:

»

Amazon’s move may have ripple effects in a way that fast food companies and other retailers haven’t because of the influence of Amazon in the corporate world and in the minds of upper-middle-class Americans. Even as Walmart has arguably been a better corporate citizen in moving its company in more of a pro-worker direction than Amazon has in recent years, Amazon is seen as an innovative and sexy technology company in a way that Walmart isn’t. Amazon making a big public move to raise worker pay will get broader cohorts of companies to do the same. Look for this as companies start to report third-quarter earnings over the next few weeks.

If $15 an hour becomes the new standard for entry-level wages in corporate America, its impact may be felt most broadly among middle-class workers. Average hourly earnings for non-managerial workers in the U.S. were $22.73 an hour in August. The historically low level of jobless claims and unemployment, combined with $15 an hour becoming an anchor in people’s minds, could make someone people earning around that $22 mark feel more secure in their jobs. Instead of worrying about losing their job and being on the unemployment rolls for a while, or only being able to find last-ditch work that pays $9 or $10 an hour, the “floor” may be seen as a $15 an hour job.

That creates a whole new set of options for middle-class households. In 2017, the real median household income in the U.S. was $61,372, which is roughly what two earners with full-time jobs making $15 an hour would make. A $15-an-hour floor might embolden some workers to quit their jobs to move to another city even without a job offer there. It might let some workers switch to part-time to focus more time on education, gaining new skills or child care.

«

Of course in the US they’d also need some confidence about health care, which is never a given when you move in the US.
link to this extract


Eleven takeaways from the NYT’s investigation into Trump’s wealth • The New York Times

Russ Buettner, Susanne Craig and David Barstow:

»

The Trumps created a company that siphoned cash from the empire.

The first major component was creating a company called All County Building Supply & Maintenance. On paper, All County was Fred Trump’s purchasing agent, buying everything from boilers to cleaning supplies. But All County was, in fact, a company only on paper, records and interviews show — a vehicle to siphon cash from Fred Trump’s empire by simply marking up purchases already made by his employees. Those millions in markups, effectively untaxed gifts, then flowed to All County’s owners — Donald Trump, his siblings and a cousin.

Lee-Ford Tritt, a leading expert in gift and estate tax law at the University in Florida, said the Trumps’ use of All County was “highly suspicious” and could constitute criminal tax fraud. “It certainly looks like a disguised gift,” he said.

All County also had an insidious downside for Fred Trump’s tenants. He used the padded invoices to justify higher rent increases in rent-regulated buildings, records show.

Mr. Harder, the president’s lawyer, disputed The Times’s reporting: “Should The Times state or imply that President Trump participated in fraud, tax evasion or any other crime, it will be exposing itself to substantial liability and damages for defamation.”

«

And there’s loads more. Trump didn’t respond to multiple requests for comment. Wonder what his up-to-date tax returns would show. Wonder if Robert Mueller is looking at those.
link to this extract


Vigilante engineer stops Waymo from patenting key lidar technology • Ars Technica

Mark Harris:

»

Following a surprise left-field complaint by Eric Swildens, the US Patent and Trademark Office (USPTO) has rejected all but three of 56 claims in Waymo’s 936 patent, named for the last three digits of its serial number. The USPTO found that some claims replicated technology described in an earlier patent from lidar vendor Velodyne, while another claim was simply “impossible” and “magic.”

Swildens, who receives no money or personal advantage from the decision, told Ars that he was delighted at the news. “The patent shouldn’t have been filed in the first place,” he said. “It’s a very well written patent. However, my personal belief is that the thing that they say they invented, they didn’t invent.”

The 936 patent played a key role in last year’s epic intellectual property lawsuit with Uber. In December 2016, a Waymo engineer was inadvertently copied on an email from one of its suppliers to Uber, showing a lidar circuit design that looked almost identical to one shown in the 936 patent…

…Remarkably, Swildens does not work for Uber or for Velodyne, nor for any other self-driving developer—he works for a small cloud computing startup. Swildens became interested in the patent when it surfaced during the Uber case, and he saw how simple Waymo’s lidar circuit seemed to be. “I couldn’t imagine the circuit didn’t exist prior to this patent,” he told Wired last year.

Swildens’ research uncovered several patents and books that seemed to pre-date the Waymo patent. He then spent $6,000 of his own money to launch a formal challenge to 936. Waymo fought back, making dozens of filings, bringing expert witnesses to bear, and attempting to re-write several of the patent’s claims and diagrams to safeguard its survival.

The USPTO was not impressed. In March, an examiner noted that a re-drawn diagram of Waymo’s lidar firing circuit showed current passing along a wire between the circuit and the ground in two directions—something generally deemed impossible.

«

As everyone on Twitter has been saying, not all heroes wear capes.
link to this extract


Star Wars: The Last Jedi abuse blamed on Russian trolls and ‘political agendas’ • The Guardian

Andrew Pulver:

»

Morten Bay, a research fellow at the University of Southern California (USC), analysed Twitter activity about the film and concluded that more than 50% of posts are by “bots, trolls/sockpuppets or political activists using the debate to propagate political messages supporting extreme rightwing causes and the discrimination of gender, race or sexuality. A number of these users appear to be Russian trolls.”

The supposed fan hostility to The Last Jedi is a well-known phenomenon, with actors such as Kelly Marie Tran experiencing extreme levels of abuse, and campaigns cropping up to lower the film’s rating on critics’ aggregators and fund a remake. However, Bay’s research indicates that not only are negative comments on social media about the film in a minority, but the “anti-Jedi” campaign has been designed to serve a wider political purpose. “The study finds evidence of deliberate, organised political influence measures disguised as fan arguments,” Bay writes. The likely objective of these measures is increasing media coverage of the fandom conflict, thereby adding to and further propagating a narrative of widespread discord and dysfunction in American society.”

«

Related: Twitter has tweaked its rules on fake accounts and behaviour ahead of the US mid-term elections. Notable (to me at least) that Del Harvey, its veep of Trust & Safety, is a co-author: she has been very busy in the past few months, having been away (literally) for some time before. Now “challenging” 9.4m accounts per week.
link to this extract


The Big Disruption • Medium

»

Something is fishy at Anahata—and it’s not just the giant squid that serves as a mascot for the world’s largest tech company. A prince in exile is working as a product manager. The sales guys are battling with the engineers. The female employees are the unwitting subjects of a wild social experiment. The VPs are plotting against each other. And the yoga-loving, sex-obsessed CEO is rumored to be planning a moon colony, sending his investors into a tizzy. Is it all downhill from here? Or is this just the beginning of a bold new phase in Anahata’s quest for global domination?

«

Jessica Powell used to work at Google. I have to say that I think it would be hard for her satire (available in its entirety on Medium, for free) to do better than The Circle.
link to this extract


This is how cyber attackers stole £2.26m from Tesco Bank customers • ZDNet

Danny Palmer:

»

the FCA’s newly published report into the Tesco Bank attack details how hackers were able to make off with over £2m over the course of 48 hours in November 2016.

The attack started at 02:00 on Saturday, 5 November 2016; by 04:00, Tesco Bank’s fraud analysis and detection system started sending automatic text messages to the bank’s personal current account holders asking them to call about “suspicious activity” on their accounts, which is how the bank itself first became aware of the attack.

As the fraud attempts increased, the calls quickly overwhelmed Tesco Bank’s fraud prevention line. Although Tesco Bank’s controls stopped almost 80% of the unauthorised transactions, the attack affected 8,261 out of 131,000 Tesco Bank personal current accounts.

The attackers most likely used an algorithm which generated authentic Tesco Bank debit card numbers and, using those virtual cards, they attempted to make thousands of unauthorised debit card transactions.

The FCA said Tesco Bank’s failures include the way in which the bank distributed debit card numbers and mistakes made in the reaction to the attack which meant that no action was taken for almost a day after the incident was first uncovered.

A number of deficiencies in the way Tesco Bank handled security left customers vulnerable to cyber attackers in an incident that was “largely avoidable”, said the FCA analysis of the incident which Tesco Bank had to this point been tight-lipped about – to the frustration of other financial institutions.

«

And 21 hours (that’s to 11pm on the day of an attack that started 0200) for the Financial Crime Operations Team to contact the Fraud Strategy Team. “In the meantime, nothing had been done to stop the attack.” Attack (or at least fake transaction) source: Brazil.

But it gets worse. Oh, yes.
link to this extract


Why a new fake news law in Singapore could be a big test for Facebook, Google, and Twitter • Buzzfeed News

Craig Silverman:

»

In early September, Kirsten Han began seeing messages on Facebook and Twitter calling her a “treacherous sow” and saying she should be executed for treason.

“You bloody rotten stinking traitors trying to get foreigners to overthrow the Singapore government and trying to destroy people live [sic] here,” read one Facebook comment. “You batch of traitors deserve death and nothing else.”

Han is a Singaporean journalist and activist, and a frequent critic of the ruling party’s approach to press freedom and use of the death penalty. She’s used to online criticism, but this was more extreme in tone and content. It also struck her as a case study in how the government itself can be a source of false allegations.

It began with a Facebook post from Han’s business partner, Ping Tjin Thum. Thum is a Singaporean academic based at the University of Oxford who was admitted to Harvard at 16 and competed in the Olympics for Singapore. He and Han run a small, member-funded nonprofit media company called New Naratif that reports on Southeast Asia and advocates for democracy in the region.

At the end of August, Han, Thum, and other activists from Singapore traveled to Malaysia to meet the newly elected prime minister. After they returned, Thum wrote on Facebook that he’d encouraged the prime minister “to take leadership in Southeast Asia for the promotion of democracy, human rights, freedom of expression, and freedom of information.”

«

It’s going to be a law that only applies to people the government doesn’t like, one suspects.
link to this extract


Apple Watch apps instantly went 64-bit thanks to obscure Bitcode option • Venturebeat

Jeremy Horwitz:

»

An obscure feature in Apple’s Xcode development software enabled Apple Watch apps to make an instant transition from 32-bit to 64-bit last month, an unheralded win for Apple Watch developers inside and outside the company. The “Enable Bitcode” feature was introduced to developers three years ago, but the Accidental Tech Podcast suggests that it was quietly responsible for the smooth launch of software for the Apple Watch Series 4 last month.

Support for Bitcode was originally added to Xcode 7 in November 2015, subsequently becoming optional for iOS apps but mandatory for watchOS and tvOS apps. Bitcode is an “intermediate representation” halfway between human-written app code and machine code. Rather than the developer sending a completely compiled app to the App Store, enabling Bitcode provides Apple with a partially compiled app that it can then finish compiling for whatever processors it wants to support.

The feature was forward-thinking enough that reports of its existence in 2015 called its most obvious use, “recompil[ing] bitcode-encoded App Store apps without any work from developers … unlikely to happen.” But that’s exactly what did happen in September 2018 with the release of the Apple Watch Series 4, which transitioned from the 32-bit Apple S3 processor to the 64-bit Apple S4. There was no waiting period for new 64-bit apps after the release of the new Watch last month, and developers didn’t even have to recompile their 32-bit apps; the apps just worked, and noticeably faster than before, on the new devices.

«

The Series 4 has a dual-core 64-bit processor, which is why 64-bit apps run faster. (The introuction of the 64-bit 5S led to 32-bit apps crashing more often.)
link to this extract


You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

Errata, corrigenda and ai no corrida: none notified
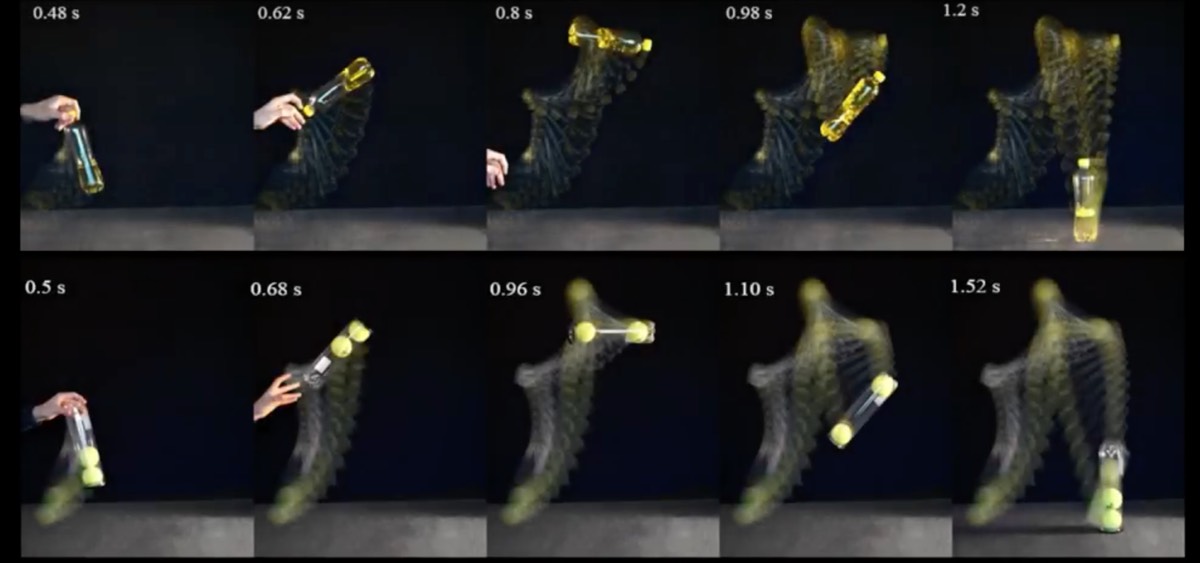
Start Up No.921: commute with Google!, stream with Google!, the Instagram penthouse, AI imaginings, and more


Revolutionary in its day, is Gmail crimping people now? Photo by Peter Forret on Flickr.

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

A selection of 10 links for you. Use them wisely. I’m @charlesarthur on Twitter. Observations and links welcome.

Google hasn’t updated Gmail, Drive, Photos storage limit in 5 years. Now what? • CNBC

Jordan Novet:

»

2013 was the most recent time Google raised the [Gmail storage] limit — bringing it up 50% to 15GB.

But now it’s been five years since Google gave free users more room for stuff. (Google did introduce free and unlimited storage of images and videos through Google Photos in 2015, but if you want that free tier, you’ll need to be okay with content getting compressed or resized.)

Google did not immediately respond to a request for comment.

My specific situation was helped along because a few years ago bought a Chromebook as a sort of backup computer. The purchase happened to come with a perk: 100GB of free storage.

But last month, Google emailed me and let me know that the extra storage would soon be going away. It turns out the promotion lasted two years.

As of today, I’m back to being just another Google account holder with 15GB of standard-issue free storage. But my data takes up more than 21GB. When I checked my Gmail inbox this morning, there was a pink banner on top instructing me to free up space or pay. In Google Drive, the icon on the left that shows how much space is left is now colored red. Conveniently there is a link below to “UPGRADE STORAGE.”

These days, through the Google One plan the company introduced this year, you can have 100GB for $19.99 per year. And $9.99 per month now gets you 2TB of storage, 100% more than before. Those prices aren’t crazy — and I understand Google’s desire to get customers paying for storage so it can grow and further diversify away from advertising — but it’s the principle of the thing.

I keep thinking back to Larry Page’s words “all the storage I need.” Did Page and others believe that would only be applicable for a few years? I hope not.

«

Gmail is the world’s biggest email service, so any increment must cost Google heftily. It’s either that, or the world’s running out of storage. (Wouldn’t that be a thing? No room left on the internet.)
link to this extract


Pushing the limits of streaming technology • Google blog

Catherine Hsiao:

»

Streaming media has transformed the way we consume music and video, making it easy to instantly access your favorite content. It’s a technically complex process that has come a long way in a few short years, but the next technical frontier for streaming will be much more demanding than video.

We’ve been working on Project Stream, a technical test to solve some of the biggest challenges of streaming. For this test, we’re going to push the limits with one of the most demanding applications for streaming—a blockbuster video game.

We’ve partnered with one of the most innovative and successful video game publishers, Ubisoft, to stream their soon-to-be released Assassin’s Creed Odyssey® to your Chrome browser on a laptop or desktop. Starting on October 5, a limited number of participants will get to play the latest in this best-selling franchise at no charge for the duration of the Project Stream test.

The idea of streaming such graphically-rich content that requires near-instant interaction between the game controller and the graphics on the screen poses a number of challenges.  When streaming TV or movies, consumers are comfortable with a few seconds of buffering at the start, but streaming high-quality games requires latency measured in milliseconds, with no graphic degradation.

«

So… it’s PC gaming except done by streaming? So you could have lower-spec PCs, and bin your console? Maybe a worry for Sony and Microsoft.
link to this extract


Microsoft Surface event 2018: 5 things to expect • The Verge

Tom Warren:

»

Microsoft is holding a media event on Tuesday in New York City. Described only as a “moment of your time,” the event is likely to focus on Surface hardware, Windows 10 features, and Microsoft’s new productivity push to win back consumers. Microsoft’s Surface chief, Panos Panay, will be attending the event and it will be the company’s first big Surface / Windows press event since former Windows chief Terry Myerson departed over the summer. It’s a chance for Microsoft to show where Windows is heading, unveil the latest Surface hardware, and perhaps surprise us with something new.

«

TL;DR: refreshes of the existing stuff, but without adding USB-C if it doesn’t already have it.
link to this extract


HP attempts to refresh the two-in-one with the leather-and-metal Spectre Folio • Ars Technica

Valentina Palladino:

»

The Spectre Folio may look like a convertible that’s covered in leather, but it’s not that simple. The leather is actually built into the PC—you can’t remove it, and HP doesn’t want you to. The leather soft chassis adheres to the magnesium and aluminum hard chassis in a construction that you won’t be able to see with your own eyes—it’s all under the surface.

While it’s classified as a convertible, it can flex into positions that were previously limited to tablets with keyboard covers. It can act as a laptop but instantly slide down into tablet mode as well. Instead of the traditional tent mode that other convertibles can achieve, the screen portion of the Spectre Folio can sit in a slot in front of the keyboard, turning it into a device ideal for photo and video viewing.

The Spectre Folio will have either an FHD or 4K touchscreen, both of which support inking, and the device will come with a stylus as well. It runs on 8th Gen Intel Core i5 and i7 Y-series processors and can support up to 8GB of RAM and 2TB of storage. HP claims the device will last at least 18 hours on a single charge. While super thin, the Spectre Folio contains two Thunderbolt 3 ports and one USB Type-C port, all of which support charging.

«

A picture (below) from The Verge shows how the keyboard is covered by the screen when you want “tablet time”; the screen can then lay flat outward, or flat inward. At least they’re trying.

link to this extract


3rd-generation Chromecast leaks ahead of Google’s launch • 9to5Google

Ben Schoon:

»

It’s been over three years since Google last refreshed its most popular product, the Chromecast. We’ve been hearing bits of information for the past few months about a possible refresh incoming, and now it seems someone has gotten their hands on the 3rd-generation Chromecast a bit early.

A Redditor posted this weekend an image of a new Chromecast he bought from a local Best Buy which was unboxed to find something that looks a bit different from a typical Chromecast. While none of the internal specifications have come out due to this leak, we can see how Google has altered the design of the beloved streaming dongle.

The comparison picture posted shows the 3rd-generation Chromecast right alongside a 2nd-generation model, and the differences are clear. Both do share the same basic design with a circular body housing the components and an HDMI cable attached to connect to the TV. According to the Redditor, this new hardware ditches the magnetic connector that allows easy management of that HDMI cable, though.

«

Over three years since the Chromecast was updated? Did they find the Platonic form, or did it hit market saturation early? (I suspect the latter.) The Chromecast has always struck me as an odd device in that it does so little for Google: it might reveal a bit of what people do at home, but it isn’t crucial to anything.
link to this extract


Take control of your commute with Google Maps • Google blog

Ramesh Nagarajan is group product manager for Google Maps:

»

Why are commutes so stressful? They’re unpredictable and long. Commute data in 25 North American cities tells us daily commute times during rush hour traffic can be up to 60% longer than what you expect when you start your drive—resulting in a lot of stress, missed meetings, and skipped breakfasts. According to historical Google Maps data, people in North America spend a full day per month commuting—which almost adds up to a two-week vacation each year.  Plus, a bad commute can negatively impact the rest of your day, long after the actual commute is over.

Today, we’re rolling out new features on Google Maps to help you take control of your daily commute— enabling you to plan ahead, prepare for the inevitable disruptions, and possibly avoid them altogether. Oh, and we’ll also help you have a bit of fun along the way…

…Sprinting to the subway station only to find that your train is delayed is our least favorite way to start the day. Now, transit riders in 80 regions worldwide will be able to see exactly where their bus or train is in real time on the map. This will help you plan your day more efficiently—you’ll know if you can spend an extra few minutes grabbing coffee, or if you really do need to make a run for it to catch your bus. And in Sydney, we’ve partnered with Transport New South Wales to show how full you next bus or train is – so you’ll know whether or not you’ll get a seat. This feature will be coming to more cities around the globe soon.

«

That’s quite a nifty feature. Open data, one assumes, so Apple could use it in time. Set a timer…
link to this extract


Fully driverless Waymo taxis are due out this year, alarming critics • Ars Technica

Timothy Lee:

»

Waymo, Google’s self-driving car project, is planning to launch a driverless taxi service in the Phoenix area in the next three months. It won’t be a pilot project or a publicity stunt, either. Waymo is planning to launch a public, commercial service—without anyone in the driver’s seat.

And to date, Waymo’s technology has gotten remarkably little oversight from government officials in either Phoenix or Washington, DC.

If a company wants to sell a new airplane or medical device, it must undergo an extensive process to prove to federal regulators that it’s safe. Currently, there’s no comparable requirement for self-driving cars. Federal and state laws allow Waymo to introduce fully self-driving cars onto public streets in Arizona without any formal approval process.

That’s not an oversight. It represents a bipartisan consensus in Washington that strict regulation of self-driving cars would do more harm than good.

“If you think about what would be required for some government body to examine the design of a self-driving vehicle and decide if it’s safe, that’s a very difficult task,” says Ed Felten, a Princeton computer scientist who advised the Obama White House on technology issues.

«

Pretty much impossible to prove “safe”. But how safe? Safer than a human? My suspicion is that they will be safer than humans in general, but do some strange things leading to accidents when humans wouldn’t have.
link to this extract


A penthouse made for Instagram • NY Times

Sapna Maheshwari:

»

This penthouse apartment in Manhattan’s SoHo neighborhood is awash in natural light, with high ceilings, gleaming hardwood floors and a rooftop deck. The living room area includes a sofa in the rosy hue known as millennial pink, the kitchen comes equipped with a floor-to-ceiling wine fridge, and the library nook is filled with books chosen for their appearance, not their contents. The white walls are spotless, and there is never any clutter.

Nobody lives here.

The 2,400-square-foot space — which rents for $15,000 a month — was designed as a backdrop for Instagram stars, who have booked it through October.

It was opened in August by Village Marketing, an agency that connects advertisers like the eyewear company Warby Parker and the Equinox fitness company to the social media personalities known as influencers. The ones who work with Village Marketing — mostly stylish young women who are paid to promote products on Instagram — have amassed huge followings with images that capture an idealized version of daily life.

«

SHOCKING! Well no, not really. Spaces reserved for modelling have existed for decades – as long as portraiture. What has happened is that Instagram has created a new slice of people who do that too. It’s a democratisation, not a debasement.
link to this extract


A wise man leaves Facebook • The New York Times

Kara Swisher:

»

When tech executives don’t like a thing I have written, I typically get a call full of gnashing teeth and why-are-you-so-mean plaintiveness. But when I recently declared on Instagram that I was sick of Instagram and had major issues with the service, [Instagram co-founder Kevin] Systrom texted and asked me why. It was neither a suck-up nor did he try to debate me.

So, I told him: It’s performative; it makes people feel badly, even if it’s beautiful; it has turned into a brag book of strivers; it is a museum and not a place to connect; it has stolen too many of its ideas from Snapchat. That said, I saw the good side, too, and wanted him to make it easier to find the many delightful things, like photographers and funny people, that made the platform joyful.

Unlike other hot-house-flower zillionaires I cover, this criticism did not slay Mr. Systrom. Maybe I am setting a low bar, but I admire him for being someone who can always take it, and that quality will be sorely missed at Facebook.

Even more important, unlike Mr. Zuckerberg, who in a recent podcast with me was unable to articulate how he felt about the high price society had paid for his success, Mr. Systrom is reflective and self-critical about the challenges that social media faces and the damage that it has done.

That was the case at a recent talk I had with him at a hopelessly hip coffee place in San Francisco, where I was left with one thought: He should be the chief executive of Facebook.

One thing he said seemed particularly wise, so I asked him if I could put it on the record, and he agreed.

“Social media is in a pre-Newtonian moment, where we all understand that it works, but not how it works,” Mr. Systrom told me, comparing this moment in the tech world to the time before man could explain gravity. “There are certain rules that govern it and we have to make it our priority to understand the rules, or we cannot control it.”

«

link to this extract


Imaginary worlds dreamed by BigGAN • Letting neural networks be weird

Janelle Shane:

»

These are some of the most amazing generated images I’ve ever seen. Introducing BigGAN, a neural network that generates high-resolution, sometimes photorealistic, imitations of photos it’s seen. None of the images below are real – they’re all generated by BigGAN.

The BigGAN paper is still in review so we don’t know who the authors are, but as part of the review process a preprint and some data were posted online. It’s been causing a buzz in the machine learning community. For generated images, their 512×512 pixel resolution is high, and they scored impressively well on a standard benchmark known as Inception. They were able to scale up to huge processing power (512 TPUv3′s), and they’ve also introduced some strategies that help them achieve both photorealism and variety. (They also told us what *didn’t* work, which was nice of them.) Some of the images are so good that the researchers had to check the original ImageNet dataset to make sure it hadn’t simply copied one of its training images – it hadn’t.

Now, the images above were selected for the paper because they’re especially impressive. BigGAN does well on common objects like dogs and simple landscapes where the pose is pretty consistent, and less well on rarer, more-varied things like crowds. But the researchers also posted a huge set of example BigGAN images and some of the less photorealistic ones are the most interesting.

«

Keep reading, though, and you’ll encounter some truly weird images. The clocks are in some ways the oddest: familiar yet wrong. How long before entire films are being generated like this? It would be like a waking dream.
link to this extract


Errata, corrigenda and ai no corrida: none notified
Start Up No.920: Berners-Lee’s new web plan, how America failed women, Facebook’s breach, US hits tech stasis, Office un-touched, and more


Do these guys think they’re going to succeed with lighting like that? Photo by Arend Kuester on Flickr.

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

A selection of 12 links for you. Why not? I’m @charlesarthur on Twitter. Observations and links welcome.

Exclusive: Tim Berners-Lee tells us his radical new plan to upend the world wide web

Katrina Brooker:

»

Ever since revelations emerged that Facebook had allowed people’s data to be misused by political operatives, Berners-Lee has felt an imperative to get this digital idyll into the real world. In a post published this weekend, Berners-Lee explains that he is taking a sabbatical from MIT to work full time on Inrupt. The company will be the first major commercial venture built off of Solid, a decentralized web platform he and others at MIT have spent years building.

If all goes as planned, Inrupt will be to Solid what Netscape once was for many first-time users of the web: an easy way in. And like with Netscape, Berners-Lee hopes Inrupt will be just the first of many companies to emerge from Solid.

“I have been imagining this for a very long time,” says Berners-Lee. He opens up his laptop and starts tapping at his keyboard. Watching the inventor of the web work at his computer feels like what it might have been like to watch Beethoven compose a symphony: It’s riveting but hard to fully grasp. “We are in the Solid world now,” he says, his eyes lit up with excitement. He pushes the laptop toward me so I too can see.

On his screen, there is a simple-looking web page with tabs across the top: Tim’s to-do list, his calendar, chats, address book. He built this app–one of the first on Solid–for his personal use. It is simple, spare. In fact, it’s so plain that, at first glance, it’s hard to see its significance. But to Berners-Lee, this is where the revolution begins. The app, using Solid’s decentralized technology, allows Berners-Lee to access all of his data seamlessly–his calendar, his music library, videos, chat, research. It’s like a mashup of Google Drive, Microsoft Outlook, Slack, Spotify, and WhatsApp.

The difference here is that, on Solid, all the information is under his control. Every bit of data he creates or adds on Solid exists within a Solid pod–which is an acronym for personal online data store. These pods are what give Solid users control over their applications and information on the web. Anyone using the platform will get a Solid identity and Solid pod. This is how people, Berners-Lee says, will take back the power of the web from corporations.

«

Hmm. Big intentions. Lot of inertia.
link to this extract


Facebook logs 90 million people out of their accounts after security breach • The Washington Post

Brian Fung:

»

The hackers were able to gain access to profile information, such as users’ names, home towns and genders, Facebook said. They may have had access to more information, but Facebook said its investigation is in the early stages. No credit card information was exposed, Facebook executives said, and so far there is no evidence that the attackers sought to access private messages or post fraudulent messages from the accounts.

“This is a serious issue, and we’re committed to addressing it,” said Facebook chief executive Mark Zuckerberg. “This underscores that there are constant attacks from people who are trying to take over accounts or steal information from people in our community.”

Facebook said it discovered the breach Tuesday after noticing a spike in user activity on Sept. 16., which prompted engineers to investigate. They found three interlocking bugs on Facebook’s website that attackers had been using to gain access to accounts.

The attackers exploited Facebook’s systems through a flaw in the company’s “View As” feature, the company said, which allows a user to view his or her own profile as somebody else might see it.

Embedded in the “View As” feature was a video uploader that was incorrectly generating security tokens — pieces of code that, under normal circumstances, are designed to let a user remain logged in even after navigating away from Facebook’s website.

«

The uploader being designed to let people send Happy Birthday messages. And those tokens, stolen, could let the hackers log into any service that used Facebook logins. The dangers of monoculture.
link to this extract


Use of internet, social media, digital devices plateaus in US • Pew Research Center

»

The shares of US adults who say they use the internet, use social media, own a smartphone or own a tablet computer are all nearly identical to the shares who said so in 2016. The share who say they have broadband internet service at home currently stands at 65% – nearly identical to the 67% who said this in a survey conducted in summer 2015. And when it comes to desktop or laptop ownership, there has actually been a small dip in the overall numbers over the last two years – from 78% in 2016 to 73% today.

A contributing factor behind this slowing growth is that parts of the population have reached near-saturation levels of adoption of some technologies. Put simply, in some instances there just aren’t many non-users left. For example, nine-in-ten or more adults younger than 50 say they go online or own a smartphone. And a similar share of those in higher-income households have laptops or desktops.

«

Notice that dip in desktop/laptop use, while tablet use inched up. Although I suspect that tablets plus smartphones have consumed that gap in PC use.

If that’s continued in two years’ time, it’ll be a clear trend. Check back in 2020!
link to this extract


Elon Musk steps down as Tesla’s chairman in settlement with S.E.C. over go-private tweet • The New York Times

Matthew Goldstein:

»

The Securities and Exchange Commission (SEC) announced the deal two days after it sued Mr. Musk in federal court for misleading investors over his post on Twitter last month that he had “funding secured” for a buyout of the electric-car company at $420 a share.

The deal with the SEC will allow him to remain as chief executive, something he could have jeopardized if he had gone to battle with the agency.

It is not clear why Mr. Musk changed his mind so quickly.

People familiar with the situation, who were not authorized to speak publicly on the matter, said lawyers for Mr. Musk and the company moved to reopen the talks with the SEC on Friday. During that time, one of Tesla’s lawyers became instrumental in securing a deal with the SEC, according to a person familiar with the negotiations.

The whipsaw events of the past few days followed a series of self-inflicted wounds by Mr. Musk.

«

Basically, someone managed to calm Musk down for long enough to tell him that he was going to lose everything if he couldn’t make a concession.

Wonder if they’ve managed to wrestle his Twitter account away from him.
link to this extract


Microsoft puts its touch-friendly Office apps for Windows 10 on hold • The Verge

Tom Warren:

»

Microsoft first started work on its touch-friendly Office apps for Windows 8.1 more than five years ago. Designed for tablets or laptops with touchscreens, the apps are lightweight and speedy versions of Word, Excel, and PowerPoint. Microsoft has updated them regularly for Windows 10, but now that the company has halted work on Windows 10 Mobile, it’s also halting work on these Office apps.

The apps aren’t fully dead yet, but Microsoft is no longer developing new features for them. “We are currently prioritizing development for the iOS and Android versions of our apps; and on Windows, we are prioritizing Win32 and web versions of our apps,” explains a Microsoft spokesperson in a statement to The Verge.

The reprioritization isn’t all that surprising given the state of dedicated universal Windows apps on Windows 10 and the Microsoft Store. These touch-friendly versions of Office were once a great example of what developers could achieve if they made universal Windows apps, but Microsoft now lets developers simply package existing desktop apps and list them in the store.

«

Meanwhile, people are saying “Apple MUST release a touchscreen Mac or it is dead!” Nope. Wasn’t true then, still isn’t true. (Touch-free version of iOS apps, as in Marzipan ones, are a different matter.)
link to this extract


How America failed women • EAnd

Imair Haque:

»

American women are severely underrepresented in positions of power — so much that it’s almost comical. America’s one of the very, very few countries, by this point in history, which has never had a female head of state. Congress is 20% women, but society is 51% women. The Senate is also 20% women, but society is 51% women. Maybe you don’t see my point. Let me make it crystal clear. In Sweden, parliament is 45% women. In Denmark, 40%. In France, 39%. In Germany, 37%. Do you see how stunning this difference is? In the rest of the rich world, women have twice as much political representation — they are almost to the point of true representational parity. But in America, women are not even half people yet, in terms of representational parity.

In fact, even in much poorer countries, women hold far more political power than American women do. In Mozambique and South Africa, women are 40% of legislators. In Vietnam, Mauritania, Kazakhstan, and Laos, 20%-30%. Do you know which country has the same number of women in political office as America? Pakistan. That’s a grim place to be, my friends — let me make it sharper precisely why.

American patriarchy has been spectacularly, singularly successful in keeping power from women. In global terms, it is one of the most successful patriarchies of all — as successful, in the most crucial ways, as a place like Pakistan. Yes, really (no, Pakistani women don’t have to wear niqabs, that’s an American fairy tale.) That lack of rights has had very real consequences, the most significant of which is that American women simply don’t hold much — or nearly enough — power in society. That was the point of refusing to ratify international conventions or constitutional amendments — not to give women rights, and therefore, to keep them relatively socially powerless.

«

Ruth Bader Ginsburg, the female Supreme Court Justice, was once asked how many women she thought should be on the court: “nine would be a good number,” she replied. (Nine is the full complement.) For how long? “Oh, only as long as men have had a majority.” (200-odd years.)
link to this extract


Hackers expose frailty of robots • Financial Times

Aliya Ram:

»

In 2017, Lucas Apa and Cesar Cerrudo, security researchers with the consultancy IOActive, showed that the version 2.5.5 of Pepper could be hacked through its software because of vulnerabilities that were discovered when it was connected to a network. They demonstrated that the robot could be controlled remotely, its limbs manipulated and its cameras used to spy on users.

Yet more than a year later, SoftBank has not patched the software, according to an analysis of its change logs by Mr Apa. He told the FT that the Japanese conglomerate had told him it could not fix the problem.

He says: “We were very disappointed by this answer, but we understand that with any new technology it is very hard for manufacturers to get the attention or investment [they need].”

SoftBank says that users were asked to maintain Wi-Fi network security and set robot passwords correctly. “We will continue to improve our security measures on Pepper, so we can counter any risks we may face,” the company says.

Pepper is just one of several robots that Mr Apa and Mr Cerrudo tested last year. They found that others, including those manufactured by UBTech Robotics, Robotis, Universal Robots, Rethink Robotics and Asratec Corp, could be hacked too.

The matter has also been raised by Bundesnetzagentur, the telecoms watchdog in Germany, which last year told parents to destroy talking dolls called Cayla because hackers could use an unsecured Bluetooth device to make the toy reveal personal data.

«

Isn’t this more like “hackers expose frailty of systems”? It’s not particularly the robots.
link to this extract


Apple looks down on ads but takes billions from Google • Bloomberg

Shira Ovide:

»

In new research, [Goldman Sachs] estimated that about $9bn of Apple’s expected 2018 services segment revenue — about one-quarter of the estimated total — has almost nothing to do with Apple itself.

Goldman estimated the $9bn is coming from Google, which pays Apple for the privilege of being the built-in search engine on Apple’s Safari web browsers, on Siri and some other spots on Apple devices. Google constantly talks about the pile of money it’s paying to Apple and others, 1 and Google investors track it fanatically. Apple, by contrast, never talks about its revenue stream from Google, and investors never seem to care about it. If Goldman’s figure is correct, however, it should dent investors’ beliefs about Apple’s business transformation, and it calls into question Apple’s moral proclamations about digital advertising.

Most estimates of Apple’s revenue from Google are more like $3bn to $4bn a year rather than double or triple that figure. But it is true that in its recent financial reports to the Securities and Exchange Commission, Apple has listed “licensing” as the first in a short list of contributors to sales growth in its services segment. “Licensing” includes the money that Apple is collecting from its search contract with Alphabet Inc.’s Google and other sources, including a legal settlement with Samsung…

…give Apple credit for not itself employing an aggressive system to harvest personal information for advertising purposes. What if instead Apple is generating one-quarter of its services revenue from enabling Google’s aggressive system of harvesting personal information for advertising purposes? Make no mistake — that is what Apple is doing by cashing those 10-figure checks from Google.

That feels worse, because Apple gets to collect a high-profit pile of money from the spoils of digital advertising without having to be accountable for the downsides of that digital advertising system. It’s perfect, and perfectly hypocritical.

«

Neil Cybart, a former Wall St analyst, poured cold water on the $9bn figure (he puts all of Licensing as less than $4bn for all of 2017). As to the “harvesting personal information” – Google doesn’t get location data from phones unless people directly consent. It can’t grab peoples’ information unless they consent. This contrasts starkly with Google tracking people on Android even when they ask it to stop.
link to this extract


What if everything we know about dark matter is totally wrong? • Wired

Katia Moskvitch:

»

Despite huge pots of money being poured since the 1970s into dark matter experiments on, under or above Earth, despite endless late nights spent doing calculations, and despite plenty of media coverage, researchers keep getting nowhere. Apart from SNOLAB, there is the LUX experiment in Lead, South Dakota, one mile underground in an abandoned gold mine. It has obtained zero results. In France, the EDELWEISS experiment in a lab under the French Alps, under 1.7 km of rock, has found nothing. The PandaX experiment in the Jin-Ping sub-terrain laboratory in China hasn’t spotted any particles either. In India, Jaduguda Underground Science Laboratory opened last year, 550 meters below the surface at an operating uranium mine. So far, they have found nothing (well, they’ve only been looking for a year). And on, and on, and on.

The leading theory is that dark matter is made out of particles that interact with normal, atomic, matter or light only through gravity – by exerting a gravitational pull. SuperCDMS will be looking for a very specific type of such exotic particles, so-called WIMPs, or weakly interacting massive particles. That’s the main (some say most obvious) dark matter candidate several detectors are searching for. Scientists are even trying to create these particles in the largest and most powerful particle accelerator in the world, the Large Hadron Collider (LHC) near Geneva (which cost nearly $7bn to build). But all in vain.

So just how much longer can researchers justify that they are looking for something unknown and finding nothing, but still get away with asking for more money to look for nothing… just a little bit longer? Well, turns out that for the researchers who have devoted their whole life to dark matter, null results are ultra-important – nearly as important as finding something.

«

If we stopped looking for dark matter, what would happen to all the dark matter articles? I mean, we’d know that the desire to write them was out there, but how would we prove it existed?
link to this extract


Instagram is deciding the future of concerts, says LeRoy Bennett • Rolling Stone

Amy X Wang:

»

Artists these days have a new concern at the forefront of their minds when designing tours and concerts: how they look not just to live audiences — but also to millions, and potentially billions, of people at home. A chief driver of that worry is Instagram.

In the last year, the social media app has added 300 million monthly active users — doubling in size and bringing its total global user count to twice the size of the population of the United States. Of that immense user base, nearly half follow 10 or more verified musicians. And even more are making regularly posts and Instagram stories about music, with concerts a particularly popular photo and video subject. “A show no longer starts when the curtain rises,” entertainment architect Ray Winkler, who designed Beyoncé and Jay-Z’s On the Run II tour, told Rolling Stone earlier this summer. “The show starts the moment the first person takes a picture of it.

As Instagram continues on its explosive growth trajectory, artists are employing all sorts of tactics ranging from practical to outlandish to ramp up the visuals of their tours and the create the perfect “Instagram moment,” says longtime concert designer LeRoy Bennett, who’s produced iconic shows for Madonna, Prince, Lady Gaga, Paul McCartney and a litany of other household names. Rolling Stone caught up with Bennett on how the trend is changing the concert industry — and where it will go from here.

«

Telling quote:

»

It can be a pain in the ass when it comes to the lighting side of things, because artists will look at these Instagrams and they get upset thinking that’s how they looked during the show when someone just took a bad photograph.

«

link to this extract


Google’s new ‘Potential Trips’ will plan a vacation for you • Condé Nast Traveler

Meredith Carey:

»

For two years, Google has been trawling through your emails for hotel bookings, flight reservations, train tickets, and more, packaging them up with a nice pretty bow in its Trips app. Now, it’s taking that personal-assistant thing one step further: by helping you plan “potential trips” in the future, piecing together the on-and-off research you’ve been doing online, Richard Holden, Google’s VP of product management, said at the Skift Global Forum in New York City this morning.

Since there are few details—it will launch on mobile in the U.S. in the “next few weeks”—Holden’s own words can explain it best. “You may have done research on Google a trip to Milan, but you haven’t actually booked it. We have all the research you’ve done—you may have starred things in Maps that you want to visit—so when you go back to Google, you’ll see ‘Upcoming trips’ but you’ll also see ‘Potential trip to Milan,’ which will show all of that recent research you’ve done, so you can pick up where you left off,” he says…

…as Traveler’s Brad Rickman wrote last year when new Trips features rolled out, it was nice to have a travel agent and partner that “actually knows something about [you]—has been there with [you], not just strolling alongside but paying attention.”

«

That is what we want out of these assistants, isn’t it? That they’ll pay attention to what we do.
link to this extract


Forget viewability: your ads aren’t serving • Ad Exchanger

Daniel Rosenblatt is in charge of Uber’s “rider display marketing”:

»

In late Q4, we launched a series of small rich-media-based mobile brand campaigns to dip our toes in the water and establish performance benchmarks. We ran the tests for a few days then reviewed the data. This health check uncovered some odd trends.

First, our click-through rates were almost zero. For in-app static 300x250s with impression and click trackers, we could sometimes see as high as 2% click-through rates (CTRs). But exciting, motion-enabled, dynamic ads were generating sub-0.10% CTRs. It just didn’t make sense. On top of that, incrementality was completely flat across various short-term metrics.

Something was wrong. We were buying significant inventory across well-known, major exchanges, but it was as if our ads weren’t being served at all.

«

When he looked into it, it turned out that publishers were saying their pages could accept any ad, even if they couldn’t; and ad networks weren’t bothering to check.

Upshot: Uber pulled all its ads from the networks that didn’t bother to check. But clearly, there are tons of ads which aren’t being shown. That saying about “50% of my money spent on advertising is wasted”? Still true online, it seems.
link to this extract


Errata, corrigenda and ai no corrida: none notified
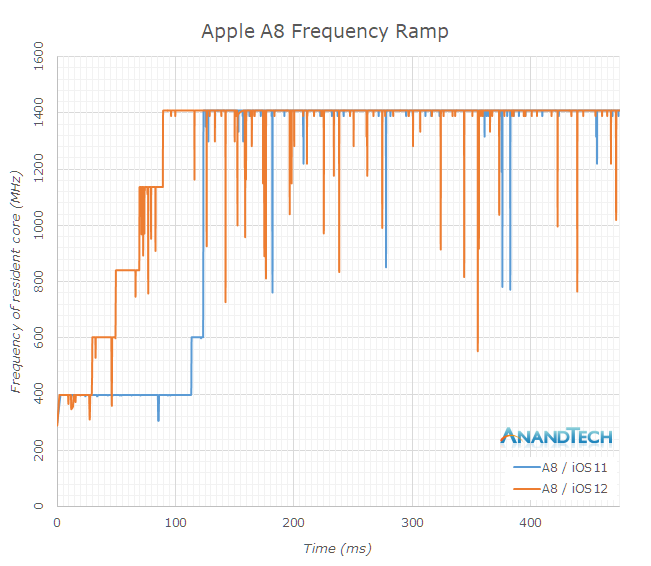
Start Up No.919: tech v democracy, Snapchat snapping?, solve your office Wi-Fi, iOS 12 + XS = fast ML, and more


Give your phone number to Facebook for two-factor authentication, and it will let advertisers target you through it. Photo by Angelos Konstantinidis on Flickr.

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.

A selection of 12 links for you. Don’t judge me, I’ll get emotional. I’m @charlesarthur on Twitter. Observations and links welcome.

The war between technology & democracy • Medium

Jamie Bartlett:

»

We rightly celebrate how the internet gives us a platform, allows new movements to form, and helps us access new information. These are good things, but don’t be blinded by to the other problems the same technology is creating. Our democracy relies on lots of boring stuff to make it actually work as a system of collective self-government that people believe in and support: a sovereign authority that functions effectively, a healthy political culture, a strong civil society, elections that people trust, active citizens who can make important moral judgements, a relatively strong middle class, and so on. We have built these institutions up over several decades — decades of analogue technology.

Now however we have a new set of technologies — digital technology — which is slowly eroding all of them. It’s not to blame one side or the other — simple to state there’s an incompatibility problem.

This structural problem is far more important than billionaires in Silicon Valley or troll farms in St Petersburg. And if we don’t find a new settlement between tech and democracy, more and more people will simply conclude that democracy no longer really works, and look for something else. This being a lecture series about dictatorship, you won’t be surprised to learn that some new form of dictatorship — a sort of gentle, benevolent data dictatorship — is the most likely candidate for replacing it. Something a little like my father’s efficient but depressing Schedule.

I’ll take three examples of how recently reported problems and explain how they are symptoms of this tech / democracy tension. Let’s start with Cambridge Analytica, one of the biggest stories of 2018, and also one of the most misunderstood.

«

Bartlett is always insightful.
link to this extract


At Snapchat, insiders question the leadership of Evan Spiegel • Wired

Katia Moskvitch:

»

Some insiders describe the atmosphere at Snap as toxic and cut-throat. It’s like “swimming in a shark tank”, says one person familiar with the company’s corporate culture. Overworked staff are being told to do jobs that they’re not skilled for, and then fired left, right and centre because they’re “incompetent”, even though in reality they lack training and are constantly stressed about whether this day could be their last.

For all its scale and notoriety, Snap is still a company that revolves around chief executive and co-founder, 28-year-old Stanford dropout Evan Spiegel, and his system of grace and favours. Are you one of the in-crowd who are invited to Spiegel’s parties? Insiders claim only a few will qualify. They say it’s an incredibly selective environment, which teaches staff to get close to their young boss and earn his appreciation. A spokesperson disputes this, saying that every employee is invited to all the major company parties.

Insiders talk of people who tried to caution Spiegel about the failed app redesign, warning it was unlikely to be popular with consumers. But still, it got rolled out. Of course, sometimes Spiegel’s intuition was right – like the idea for Snapchat’s famous vanishing messages. Lots of people cautioned him against it, but it worked. Maybe it’s this experience that has made Spiegel tend towards an instinctive mistrust of advice, whether good or bad.

The rot seems to go deep. Over the past few months, Snap has been plagued by a long list of executive defections. In January, vice president of product Tom Conrad cleaned up his desk. The company’s chief of engineering, Stuart Bowers, left in May to join Tesla. Chief financial officer Drew Vollero bolted the same month and was replaced by former Amazon executive Tim Stone. Chief strategy officer Imran Khan is the latest to go, announcing he will soon leave after three years at the company. Similar claims about Snap’s corporate culture have also been published by The Information and Bloomberg.

«

It’s even got a name: “founder’s syndrome”. A bit like music’s “Lead Singer’s Disease”. (Lead as in dogs, not the metal.)
link to this extract


Facebook is giving advertisers access to your shadow contact information • Gizmodo

Kashmir Hill:

»

Last week, I ran an ad on Facebook that was targeted at a computer science professor named Alan Mislove. Mislove studies how privacy works on social networks and had a theory that Facebook is letting advertisers reach users with contact information collected in surprising ways. I was helping him test the theory by targeting him in a way Facebook had previously told me wouldn’t work. I directed the ad to display to a Facebook account connected to the landline number for Alan Mislove’s office, a number Mislove has never provided to Facebook. He saw the ad within hours.


What Facebook told Alan Mislove about the ad I targeted at his office landline number
Screenshot: Facebook (Alan Mislove)

One of the many ways that ads get in front of your eyeballs on Facebook and Instagram is that the social networking giant lets an advertiser upload a list of phone numbers or email addresses it has on file; it will then put an ad in front of accounts associated with that contact information… Facebook calls this a “custom audience.”

…Giridhari Venkatadri, Piotr Sapiezynski, and Alan Mislove of Northeastern University, along with Elena Lucherini of Princeton University, did a series of tests that involved handing contact information over to Facebook for a group of test accounts in different ways and then seeing whether that information could be used by an advertiser. They came up with a novel way to detect whether that information became available to advertisers by looking at the stats provided by Facebook about the size of an audience after contact information is uploaded. They go into this in greater length and technical detail in their paper.

They found that when a user gives Facebook a phone number for two-factor authentication or in order to receive alerts about new log-ins to a user’s account, that phone number became targetable by an advertiser within a couple of weeks.

«

That two-factor authentication detail is truly shocking.
link to this extract


Ex-Google employee urges lawmakers to take on company • The New York Times

Kate Conger:

»

In a harshly worded letter sent this week, the former employee, Jack Poulson, criticized Google’s handling of a project to build a version of its search engine that would be acceptable to the government of China. He said the project was a “catastrophic failure of the internal privacy review process.”

He said lawmakers should increase transparency and oversight of the company and technology industry, saying that there is a “broad pattern of unaccountable decision making.”

Dr. Poulson left the company after news articles revealed the existence of the project last month. It was first reported on by the Intercept news site.
Google’s chief privacy officer, Keith Enright, testified on Wednesday before a congressional committee about the company’s approach to data protection. Executives from Apple, AT&T, Amazon, Twitter and Charter Communications also appeared at the hearing.

Dr. Poulson said the Chinese project, called Dragonfly, had several “disturbing components.” A prototype, he said, would allow a partner company in China to view a person’s search history based on his or her phone number. He said the project also censored an extensive list of subjects that included information about air quality and China’s president, Xi Jinping…

Google left China in 2010, denouncing government censorship. That year the company also said it had discovered that Chinese hackers had attacked the company’s corporate infrastructure.

“It should be pretty obvious that they should be asked what changed between 2010 and today,” said Cynthia Wong, a senior researcher at Human Rights Watch.

«

That last one is a zinger, it must be said.
link to this extract


How Triplebyte solved its office Wi-Fi problems • Triplebyte Blog

Mike Robbins:

»

Our team just moved to a larger office in downtown San Francisco. On moving day, I was shocked to discover a bundle of rough-cut unterminated ethernet cables on one end, ripped-out punch-down jacks on the other, no uplink, and no Wi-Fi!

There’s no IT team at startups, and as software engineers, we might be called on to step up in a pinch. Here’s a smorgasbord of suggestions — some well-known and others obscure — that helped me get a reliable network running fast.

«

These are all fascinating discoveries – especially about how to get the same Wi-Fi network to appear to be all over the office.
link to this extract


Bizarre particles keep flying out of Antarctica’s ice, and they might shatter modern physics • Live Science

Rafi Letzer:

»

Physicists don’t know what it is exactly. But they do know it’s some sort of cosmic ray — a high-energy particle that’s blasted its way through space, into the Earth, and back out again. But the particles physicists know about — the collection of particles that make up what scientists call the Standard Model (SM) of particle physics — shouldn’t be able to do that. Sure, there are low-energy neutrinos that can pierce through miles upon miles of rock unaffected. But high-energy neutrinos, as well as other high-energy particles, have “large cross-sections.” That means that they’ll almost always crash into something soon after zipping into the Earth and never make it out the other side.

And yet, since March 2016, researchers have been puzzling over two events in Antarctica where cosmic rays did burst out from the Earth, and were detected by NASA’s Antarctic Impulsive Transient Antenna (ANITA) — a balloon-borne antenna drifting over the southern continent.

ANITA is designed to hunt cosmic rays from outer space, so the high-energy neutrino community was buzzing with excitement when the instrument detected particles that seemed to be blasting up from Earth instead of zooming down from space. Because cosmic rays shouldn’t do that, scientists began to wonder whether these mysterious beams are made of particles never seen before.

«

As long as it’s only particles, I’m OK with it.
link to this extract


Crypto mining giant Bitmain reveals heady growth as it files for IPO • TechCrunch

Jon Russell:

»

After months of speculation, Bitmain — the world’s largest provider of crypto miners — has opened the inner details of its business after it submitted its IPO prospectus with the Stock Exchange of Hong Kong. And some of the growth numbers are insane.

The document doesn’t specify how much five-year-old Bitmain is aiming to raise from its listing — that’ll come later — but it does lift the lid on the incredible business growth that the company saw as the crypto market grew massively in 2017. Although that also comes with a question: can that growth continue in this current bear market?

The company grossed more than $2.5bn in revenue last year, a near-10X leap on the $278m it claims for 2016. Already, it said revenue for the first six months of this year surpassed $2.8bn.

Bitmain is best known for its ‘Antminer’ devices — which allow the owner to mine for Bitcoin and other cryptocurrencies — and that accounts for most of its revenue: 77% in 2016, 90% in 2017, and 94% in the first half of 2018.

«

Great that bitcoin has finally got rid of all that nasty centralisation.
link to this extract


iOS 12 Core ML benchmarks • Heartbeat

Jameson Toole:

»

At Fritz, we collect performance data every time a model is run on a user’s device to make sure that experiences are consistent. I went and looked at real world data from our open-source Heartbeat app to see how each Apple device stacked up.


Core ML performance by device. Higher is better. Note the y-axis is logarithmic. Data from Fritz.

This Core ML model runs over 10X faster on the A12 processor in the iPhone XS Max compared with the iPhone X. The model above performs object detection, and results vary from model to model. The smallest speed-up I saw was around 5x. I also found it interesting that the A10X Fusion processor in the 2018 iPad beat out the iPhone X. In other benchmarks, the processors appear fairly similar, but perhaps there are differences in memory.

«

That’s incredible: a 10-fold increase in a generation. From iOS 11 to iOS 12, there’s a 38% increase in speed for these models. Toole concludes:

»

We’re just at the beginning of an incredible wave of mobile experiences powered by on-device machine learning. Processors like the A12 are going to make it happen.

«

link to this extract


Lessons from losing a week of photos to memory card failure • QT Luong’s Blog

Mr Luong:

»

Landscape expeditions can be taxing in the long days of summer, even more so if you are also doing night photography. After flying to Seattle, I arrived at the coast of Olympic National Park around 11 PM – many view Treasured Lands as a culmination of my work in the national parks, but I am far from being done with them! Seeking stars, I woke up before 2 AM for the short window between moonset and astronomical twilight. However, the marine layer had rolled in while I was hiking to the beach, and I shivered until past sunrise time without even seeing a sliver of sky. The next day, since I had to drive from Heart of the Hills Campground and hike 45 minutes to Hurricane Hill, I rose before 1 AM.

[He captured a beautiful shot. Click through the headline to see it.]

On the last day, temperatures in the inland plains of Hanford Reach rose above 100F. When I came home from the week-long trip, I went straight to bed. The next morning, I reached for my cameras, took the memory card out, and inserted into the card reader. This resulted in the dreaded…

«

Uh-oh. Though his experience was very unusual.
link to this extract


Fancy Bear, the Russian election hackers, have a nasty new weapon • Daily Beast

Kevin Poulsen:

»

The malware, uncovered by the European security company ESET, works by rewriting the code flashed into a computer’s UEFI chip, a small slab of silicon on the motherboard that controls the boot and reboot process. Its apparent purpose is to maintain access to a high-value target in the event the operating system gets reinstalled or the hard drive replaced—changes that would normally kick out an intruder.  

It’s proof that the hackers known as Fancy Bear “may be even more dangerous than previously thought,” company researchers wrote in a blog post. They’re set to present a paper on the malware at the Blue Hat security conference Thursday…

…The first public whiff of Russia’s new malware emerged last March, when Arbor Networks’ ASERT team reported finding malware designed to look like a component of the theft-recovery app Absolute LoJack.

Absolute LoJack works much like Apple’s Find My iPhone app, allowing laptop owners to attempt to geo-locate a computer after a theft, or to remotely wipe their sensitive files from the missing machine. The hackers copied one piece of the app, a background process that maintains contact with Absolute Software’s server, and changed it to report to Fancy Bear’s command-and-control servers instead.

ESET researchers call the malware LoJax. They suspected they were seeing just one piece of a larger puzzle, and started looking for additional LoJax components in Eastern Europe and the Balkans, where LoJax was popping up on hacked machines alongside better-known Fancy Bear implants like Seduploader, X-Agent, and X-Tunnel.

They found a new component of LoJax designed to access technical details of a computer’s UEFI chip, and surmised that Fancy Bear was moving to the motherboard. Eventually they found the proof in another component called “ReWriter_binary” that actually rewrote vulnerable UEFI chips, replacing the vendor code with Fancy Bear’s code.

«

link to this extract


Marzipan • Benjamin Mayo

The aforementioned Mayo on the layer that gets iOS apps to be rewritten for MacOS:

»

Marzipan apps are ugly ducklings. As soon as you use them, you can just know these are not at one with the system. You detect that there’s a translation layer of some kind at work here, just like when you use Slack on the Mac you instinctively feel that it’s a web app in a thin wrapper. The underlying implementation is exposed to the user with a bevy of performance sluggishness, UI quirks and non-standard behaviours. That’s bad.

I launch News. I see a window with a reasonable lineup of platform-standard toolbar controls, although I notice that the title of the window is ‘News’. This is a little odd as modern Mac design generally means that the application name is not repeated in the window itself. The title represents the active visible content inside the window, or they simply might not have a visible title at all. Not a universal rule, but certainly not the norm.

Then, only a few pixels down the screen, is the words Apple News repeated again, this time in all-caps. ‘News’ in the menubar, ‘News’ in the titlebar, ‘Apple News’ in the sidebar. Is the word News redundantly displayed in these three different places because that’s what makes sense for the Mac UI? I’d wager it is not a design choice. I think it’s pretty clear that Apple News is in the sidebar because the sidebar is a wholesale port of the iPad interface. iOS on the iPad doesn’t have a menubar or a titlebar, so it isn’t uncommon for apps to put their branding in the app itself. Why is News in the titlebar? In this case, I suspect the Marzipan system houses apps in a window with a titlebar, and it automatically populates the window with the display name of the bundle. Home is the only app of the new set that bucks this pattern, instead using a segmented control as the centred toolbar item.

This first point is arguably a nitpicky detail, but it’s emblematic of the problem I have with these apps.

«

Being nitpicky is not just for mobile OS users. When something just looks wrong, it bugs people.
link to this extract


Tariffs start to drag on US economy as trade deficit widens • Bloomberg

Sho Chandra:

»

Economists at Amherst Pierpont Securities and Capital Economics trimmed their estimates for gross domestic product growth this quarter. Before Thursday’s data, the median estimate in a Bloomberg survey was for 3% expansion.

While analysts said the trade deficit partly reflected an expected drop in soybean exports following a second-quarter surge ahead of Chinese-imposed tariffs, and economic growth is projected to remain solid, the numbers illustrate how the trade war is spurring volatility in the data. In addition, the widening deficit runs contrary to Trump’s aim of a narrower gap and underscores the challenges of achieving that goal amid strong domestic demand — which tends to boost imports — and retaliatory tariffs from abroad.

“The data are grim,” Ian Shepherdson, chief economist at Pantheon Macroeconomics Ltd., said in a note, referring to the August goods trade gap. “The administration’s narrative, that the second-quarter drop in the deficit was a result of their trade policies, has now fallen apart, as it was always likely to do.”

…While economists say it may be too early to detect the exact impact from trade disputes, the data bear watching as the headwind and uncertainty look unlikely to dissipate. Thursday’s reports come after the US and China imposed tariffs on each other in late August, which followed others implemented in early July. The US added tariffs on another $200bn of Chinese imports this week – the largest escalation of the trade war so far.

«

This is only the effects of the very earliest tariffs, from July and a little from August. The bigger impact is yet to come. Though economists will be delighted to have a laboratory where they can demonstrate what tariffs do to an economy.
link to this extract


Errata, corrigenda and ai no corrida: none notified
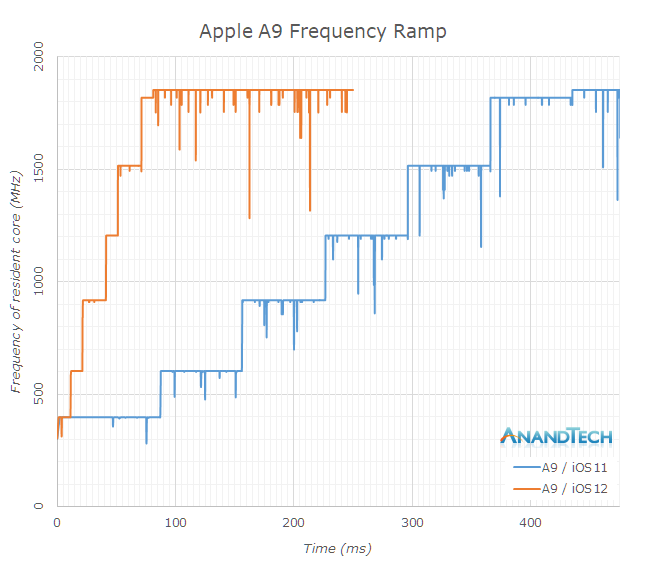
Start Up No.918: WhatsApp co-founder vents, FB Messenger chief vents back, the good-bad Apple News news, is Shazam an AR trojan horse?, and more


This iconic potato peeler came from a radical realisation about users. Photo by Andy Melton on Flickr.

A selection of 11 links for you. J’accuse! I’m @charlesarthur on Twitter. Observations and links welcome.

Apple News is giving the media everything it wants—except money • Slate

Will Oremus:

»

Sources at several news outlets say they’ve seen their audience on Apple News multiply in 2018 alone. Some now say it has become one of their top traffic sources, alongside Facebook and Google. At Slate, which disclosed its data for this story, page views on Apple News have roughly tripled since September 2017, and the app recently surpassed Facebook as a driver of readership.

Conversations with social media consultants and people who work in audience development at major publications, along with recent reports by other outlets, suggest Slate is not an outlier—which is why many news organizations are now making Apple News an important part of their strategy to reach as large an audience as possible.

There is, of course, a catch. Whereas Facebook sent hordes of readers from its news feed to publishers’ websites, Apple tends to keep them inside its app. And so far, publishers have found that’s not a lucrative place to be. Although Apple allows publishers to sell ads within their stories—and partnered two years ago with NBCUniversal to sell “backfill” ads in slots that the publishers don’t fill themselves—several sources at media outlets told me that they’re seeing little to no revenue from Apple News.

The problem, publishers say, is that the NBCUniversal partnership isn’t yielding much money, and Apple doesn’t make it particularly easy for publishers to fill their own unsold inventory. Apple News doesn’t support some of the common ad systems that dominate ad sales on the web, and not all media companies find it worthwhile to develop and sell ads specifically for Apple News. (Those that do can keep all the revenue or they can let Apple sell them, in which case Apple takes a 30% cut.) As Matt Karolian, the Boston Globe’s director of new initiatives, told me, “The juice ain’t worth the squeeze.”

«

Oremus calculates that “Slate makes more money from a single article that gets 50,000 page views on its site than it does from the 6 million page views it receives on Apple News in an average month.”
link to this extract


Watch out, algorithms: Julia Angwin and Jeff Larson unveil The Markup, their plan for investigating tech’s societal impacts • Nieman Journalism Lab

Christine Schmidt interviewed Julia Angwin, who left ProPublica to set up the new site:

»

ANGWIN: …We have an idea about how journalism should be. It’s much more tech-focused than any newsroom, even though ProPublica is the most tech-infused newsroom out there. We want to take it to another level.

SCHMIDT: What is that next level? What are the nuts and bolts of how this organization will operate differently?

ANGWIN: We describe ourselves as doing journalism that is based on the scientific method. The idea is that objectivity has been a false god for journalism for a long time. It started out as a decent idea, but it’s led to a lot of what people call false equivalents. I think journalism needs a new guiding light, a new philosophical approach, and I think that approach should be the scientific method. What that really means is we develop a hypothesis. Maybe the hypothesis is: ‘Brett Kavanaugh. Did he actually harass a woman or not?’ Then you collect evidence — how much evidence is there for and against this. Then you describe the limitations of your evidence: ‘So far the evidence is only one/two people.’
It doesn’t have to be ‘he said, she said.’ It’s more about: this is the amount of evidence to support this hypothesis, and then here are the limitations of this. There are always limitations to our findings. Even though climate change is well accepted scientifically, there are limitations for those findings as well. That’s our goal, to try to frame our journalism around that.

What that means in practice is having people with technical and statistical skills involved in an investigation from the outset. So much of what happens in traditional newsrooms, in every newsroom I’ve ever worked in, is that there’s a data desk. A reporter goes over to the desk and basically orders data like it’s a hamburger. Usually by then, the reporter has already done the reporting and has a hypothesis based on the anecdotes. Then, if the data doesn’t support it, there’s a fight between them and the data desk. Or, more often, there’s not even data available.

«

This sounds fantastic. (Not for everyone, of course.) Data journalism – where the story comes from the data – is enormously satisfying when it comes right. Some of my best stories have come from interpreting public documents: the story’s in there, you just have to listen to what the numbers are saying.
link to this extract


A history of the OXO Good Grips peeler • Fast Company

Mark Wilson heard the story of how the thick-handled swivel peeler was designed, told by Davin Stowell, talking about the designer Sam Farber:

»

[Farber] and his wife Betsey spent a month cooking and enjoying the French countryside. One night I’m in my office, it’s 7:30 p.m., and I get a call from Sam. He’s in France, where its 1:30. in the morning, and he’s incredibly excited.

He was cooking with Betsey, she had arthritis, and she was complaining about the peeler, complaining that it was hurting her hands. As I remember, it was an apple tart, though Betsey claims it wasn’t an apple tart. But that’s what Sam claimed to me.

She was frustrated. The old-style metal peeler wasn’t good. Her background was in architecture and design. I think she initiated the idea of, “Sam, can you do something about this? Make a better handle.” She grabbed some clay and started on her own. She recognized: “This is something that could be made better, and my husband used to be a housewares executive, and he should do something about it.” She was very involved in looking at things, trying things, and giving her input along the way.

It instantly dawned on him, here’s an opportunity to make a product. Nothing had really been done in a serious way with kitchen gadgets. They were either cheap items that didn’t work very well, or if they were more expensive, they might be designed with a steel instead of plastic handle, but they didn’t actually work any better than the cheap stuff.

Here’s something he could do to help people, he thought. So he wanted me to get started on it immediately. He knew he had to do a full line of tools. It couldn’t be just a peeler, it had to be 15 to 20 different tools so it could occupy enough wall space at retail to get attention.

«

Large-handled grips seems so obvious in retrospect, but you need designers who are working with people who have arthritis for it to be obvious when it’s not there.
link to this extract


Exclusive: WhatsApp cofounder Brian Acton gives the inside story on #DeleteFacebook and why he left $850m behind • Forbes

Parmy Olson, with a hell of a scoop – and what timing:

»

“At the end of the day, I sold my company,” Acton says. “I sold my users’ privacy to a larger benefit. I made a choice and a compromise. And I live with that every day.”

Despite a transfer of several billion dollars, Acton says he never developed a rapport with Zuckerberg. “I couldn’t tell you much about the guy,” he says. In one of their dozen or so meetings, Zuck told Acton unromantically that WhatsApp, which had a stipulated degree of autonomy within the Facebook universe and continued to operate for a while out of its original offices, was “a product group to him, like Instagram.”

So Acton didn’t know what to expect when Zuck beckoned him to his office last September, around the time Acton told Facebook brass that he planned to leave. Acton and Koum had a clause in their contract that allowed them to get all their stock, which was being doled out over four years, if Facebook began “implementing monetization initiatives” without their consent.

To Acton, invoking this clause seemed simple. The Facebook-WhatsApp pairing had been a head-scratcher from the start. Facebook has one of the world’s biggest advertising networks; Koum and Acton hated ads. Facebook’s added value for advertisers is how much it knows about its users; WhatsApp’s founders were pro-privacy zealots who felt their vaunted encryption had been integral to their nearly unprecedented global growth.

This dissonance frustrated Zuckerberg. Facebook, Acton says, had decided to pursue two ways of making money from WhatsApp. First, by showing targeted ads in WhatsApp’s new Status feature, which Acton felt broke a social compact with its users. “Targeted advertising is what makes me unhappy,” he says. His motto at WhatsApp had been “No ads, no games, no gimmicks”—a direct contrast with a parent company that derived 98% of its revenue from advertising. Another motto had been “Take the time to get it right,” a stark contrast to “Move fast and break things.”

«

The lawyer who was there with Zuck disagreed about the clause. So Acton left, with $850m of shares unvested. He had preferred a “metered” system for monetising WhatsApp – you’d pay per message past a certain number. Sheryl Sandberg said “it won’t scale”. (To be honest, I agree with her.)

There’s lots more fascinating detail in this piece. Very instructive about how Facebook has changed.
link to this extract


The other side of the [WhatsApp] story • David Marcus on Facebook

Marcus, former head of Facebook Messenger, introduced this Facebook posting with a tweet saying “I just couldn’t take it any more, so here’s the other side of the story Brian Acton has been telling”:

»

WhatsApp founders requested a completely different office layout when their team moved on campus. Much larger desks and personal space, a policy of not speaking out loud in the space, and conference rooms made unavailable to fellow Facebookers nearby. This irritated people at Facebook, but Mark personally supported and defended it.

Second — on encryption. The global roll-out of end-to-end encryption on WhatsApp happened after the acquisition, and with Mark’s full support. Yes, Jan Koum played a key role in convincing Mark of the importance of encryption, but from that point on, it was never questioned. I witnessed Mark defending it a number of internal meetings where there was pushback — never for advertising or data collection reasons but for concerns about safety — and even in Board Meetings. Mark’s view was that WhatsApp was a private messaging app, and encryption helped ensure that people’s messages were truly private.

Third — on the business model. I was present in a lot of these meetings. Again, Mark protected WhatsApp for a very long period of time. And you have to put this in the context of a large organization with businesses knocking on our door to have the ability to engage and communicate with their customers on WhatsApp the same way they were doing it on Messenger. During this time, it became pretty clear that while advocating for business messaging, and being given the opportunity to build and deliver on that promise, Brian actively slow-played the execution, and never truly went for it. In my view, if you’re passionate about a certain path — in this case, letting businesses message people and charging for it — and if you have internal questions about it, then work hard to prove that your approach has legs and demonstrate the value. Don’t be passive-aggressive about it. And by the way the paid messaging that WhatsApp is rolling out now sounds pretty similar to metered messaging from my point of view…

«

He also calls Acton “low-class” for attacking Facebook, “the company and people that made you a billionaire”.

Also well worth reading: ex-purchased-by-Facebook-startup-person-who-exited Antonio Garcia Martinez weighs in with a Twitter thread about the differences between Acton and Marcus.
link to this extract


Facebook’s recent ‘bear hug’ of Instagram frustrated its independent founders • Recode

Kurt Wagner:

»

Over the past year, both Systrom and Krieger have grown increasingly frustrated and agitated with Zuckerberg and Facebook’s increased influence over the app, according to multiple sources. One characterized it as “bizarre meddling” that hurt morale within the unit.

Specifically, there were worries that Facebook’s moves were hurting the app’s growth — perhaps even intentionally — through some of the company’s product updates and marketing changes, these sources said.

That included a throttling back of Instagram’s promotion inside the Facebook app, apparently ordered by Zuckerberg, that dropped weekly referrals significantly by hundreds of thousands of users.

Systrom was also frustrated with a recent Facebook change to how posts are shared between the two apps. Previously, photos shared to Facebook via Instagram included a label identifying the photo as an Instagram photo, presumably to encourage people to visit or download Instagram. That label was recently removed, which made it appear as though people were posting those photos directly to Facebook and not to Facebook via Instagram.

It was a small tweak, but it was a big deal inside of Instagram, according to multiple sources. Systrom — who has historically been hands-on with all the aspects of the app — disagreed with the decision, and even posted as much on the internal company Facebook page. The feeling of some was that Facebook wasn’t promoting Instagram, and even taking credit for engagement that Instagram was driving.

«

This take makes a lot of sense. Systrom might have taken a lot, but feeling that his (joint) creation was being ignored, having done the hard work of seeing off Snapchat, must surely have rankled.

And he left just before the next big problem…
link to this extract


Instagram has a drug problem. Its algorithms make it worse • The Washington Post

Elizabeth Dwoskin:

»

Recent searches on Instagram, which is owned by Facebook, for hashtags of the names of drugs — such as #oxy, #percocet, #painkillers, #painpills, #oxycontin, #adderall and #painrelief — revealed thousands of posts by a mash-up of people grappling with addiction, those bragging about their party going lifestyle and enticements from drug dealers.

Following the dealer accounts, or even liking one of the dealer posts, prompted Instagram’s algorithms to work as designed — in this case, by filling up a person’s feed with posts for drugs, suggesting other sellers to follow and introducing new hashtags, such as #xansforsale. Ads from some of the country’s largest brands, including Target, Chase and Procter & Gamble, as well as Facebook’s own video streaming service, appeared next to posts illegally selling pills.

Even as top executives from Facebook and Twitter, which has also long struggled with posts offering drugs illegally, promised earlier this month in a congressional hearing that they were cracking down on sales of opioids and other drugs, their services appeared to be open marketplaces for advertising such content. Facebook’s chief operating officer, Sheryl Sandberg, said her company was “firmly against” such activity. Twitter chief executive Jack Dorsey said he was “looking deeply” at how drug-selling spreads on the site.

But activists and other groups have warned tech companies about illegal drug sales on their platforms for years. In recent months, lawmakers, the Food and Drug Administration and some advertisers have stepped into the fray. In April, FDA Commissioner Scott Gottlieb charged Internet companies with not “taking practical steps to find and remove opioid listings.” Sen. Joe Manchin III (D-W.Va.) called social media companies “reckless,” saying, “It is past time they put human life above profit and finally institute measures that crack down on these harmful practices, preventing the sale of illegal narcotics on or through their platforms.”

«

link to this extract


Why did Apple spend $400M to acquire Shazam? • Apple Insider

Daniel Eran Dilger:

»

in 2016, Shazam’s new foray into marketing was compelling enough to raise $30m in new funding from investors, giving the company a unicorn valuation of $1bn. The fact that Apple subsequently paid “only” $400m for it makes the deal sound like a bargain.

Last year, Shazam made an additional step, embracing Augmented Reality. Now, rather that just taking users to a standard website, it could use its Shazam Codes (or visual recognition of products or posters) to launch an engaging experience right in the camera, layering what the camera sees with “augmented” graphics synced to the movement of the user’s device.

Now users could identify a bottle of Bombay Sapphire gin and see it animate botanicals in front of them, while also suggesting cocktail recipes.

Another Shazam campaign in Australia, for Disney’s “Guardians of the Galaxy 2,” delivered a Spotify playlist “mixtape” along with presenting the movie trailer and an opportunity to buy tickets. A campaign in Spain let users animate Fanta billboards in AR using their phones. And a Hornitos tequila app used a mini-game, rendered in ARKit, to award discounts on purchases.

Given Apple’s interest in building traction for ARKit, which launched last fall as the world’s largest AR platform, it seems pretty clear that Apple bought Shazam, not really for any particular technology as Apple has already developed its own core visual recognition engine for iOS, but because Shazam has developed significant relationships with global brands to make use of AR as a way to engage with audiences.

«

Hmm. The valuation for Shazam was always a bit dubious, though as he points out the $400m is (by Apple’s standards) a lot of money. If Apple really wants Shazam for its AR (and let’s face it, the purchase price wouldn’t make sense if it’s just on music recognition) then things got interesting.
link to this extract


Compal to begin production of Apple Watch Series 4 • Digitimes

Aaron Lee and Adam Hwang:

»

With Quanta Computer’s capacity for the Apple Watch Series 4 at its factory in Changshu, eastern China fully loaded, the wearable’s second supplier Compal Electronics reportedly will begin mass production of the smartwatch in November 2018, according to industry sources.

Quanta and Compal both declined to comment on its clients or orders.

Some market watchers noted that Apple sold around 4.2 million Apple Watches worldwide in the second quarter of 2018 and the device’s global shipments are estimated to arrive at 18.0-19.5m units in 2018. Currently, the Apple Watch has a share of 35% in worldwide smartwatch shipments.

«

I’d ignore the numbers in there (the “share” depends on who you ask, as does the total) and focus on the fact: Apple’s got one factory now making Watches at its full capacity, and it’s getting a second online. That means it expects to sell a very great many more in the coming months – which, given the larger screen and faster processor and better waterproofing, wouldn’t be a surprise. Remember how you didn’t see anyone wearing AirPods, and now you do? Going to be the same with the Watch.
link to this extract


Google promises Chrome changes after privacy complaints • CNET

Stephen Shankland:

»

“We’ve heard — and appreciate — your feedback from the last few days, and we’ll be making some product changes,” tweeted Parisa Tabriz, a security team leader at Google.

Google added in a blog post Tuesday evening that it will add new options and explanations for its interface and reverse one Chrome cookie-hoarding policy that undermined people’s attempts to clear those cookies.

The situation shows the difficulties Google faces offering both the most widely used browser and one of the most powerful online advertising empires. Chrome is a powerful tool that lets websites gather the kind of personal information that makes it possible for advertisers to target ads for a particular audience. But Google operates some of the biggest online sites out there, and Chrome itself, if unfettered, has a view into our most private online activity.

«

It also – in the current version – doesn’t delete Google signin cookies even if you try to clear the cookies in Chrome. Which means Google can keep tracking you. (This was the subject of the Safari cookie lawsuit in the UK, and the US, where Google hacked Safari so that a Google signin would also be a DoubleClick advertising signin.)
link to this extract


Why were lettuce supply chains in the New York Times? • Bloomberg Gadfly

Matt Levine on that IBM-Walmart story from Tuesday:

»

the more complicated challenge is that Walmart wants to track lettuce not only when it is in Walmart’s hands but also at every step of the supply chain: “By this time next year, more than 100 farms that supply Walmart with leafy green vegetables will be required to input detailed information” into the database. This is not a big technological problem—it’s just some more inputs to the database—but it is a logistical and contractual problem. Walmart has to get its suppliers to agree (and to get their suppliers to agree, etc.) to make inputs into the database, and teach them how to use it, and give them passwords, and check that they are inputting information correctly. Database design is an element of the solution here—you want to make the database easy to use and hard to mess up, and you want to give the suppliers access rights only to input data about their lettuce, while only Walmart (and IBM) has the complete view of the whole supply chain—but it is not necessarily the hardest part; the hard part is the social and commercial work of getting the farmers to agree to do a new annoying thing. If you are Walmart, though, I guess that part’s not so hard either: The farmers really want to sell to you, so they’ll jump through some hoops.

Anyway it is all pretty interesting, as a case study in supply-chain management and database design, but I have to say that you don’t generally read a lot of stories about supply-chain management and database design in the New York Times. I can’t quite figure out why they were interested in this one. Can you?

«

That’s right, it’s because it used the chainblock. Have I got the jargon right?
link to this extract


Errata, corrigenda and ai no corrida: none notified

You can sign up to receive each day’s Start Up post by email. You’ll need to click a confirmation link, so no spam.